Why We Run Wazuh: Open-Source SIEM That Punches Above Its Weight
Why We Run Wazuh: Open-Source SIEM That Punches Above Its Weight Most organizations under 2,000 employees do not have an […]

Why We Run Wazuh: Open-Source SIEM That Punches Above Its Weight Most organizations under 2,000 employees do not have an […]
Logged But Never Reviewed: The HIPAA Monitoring Failure Behind OCR’s Latest Settlements A phishing email compromised one employee email account
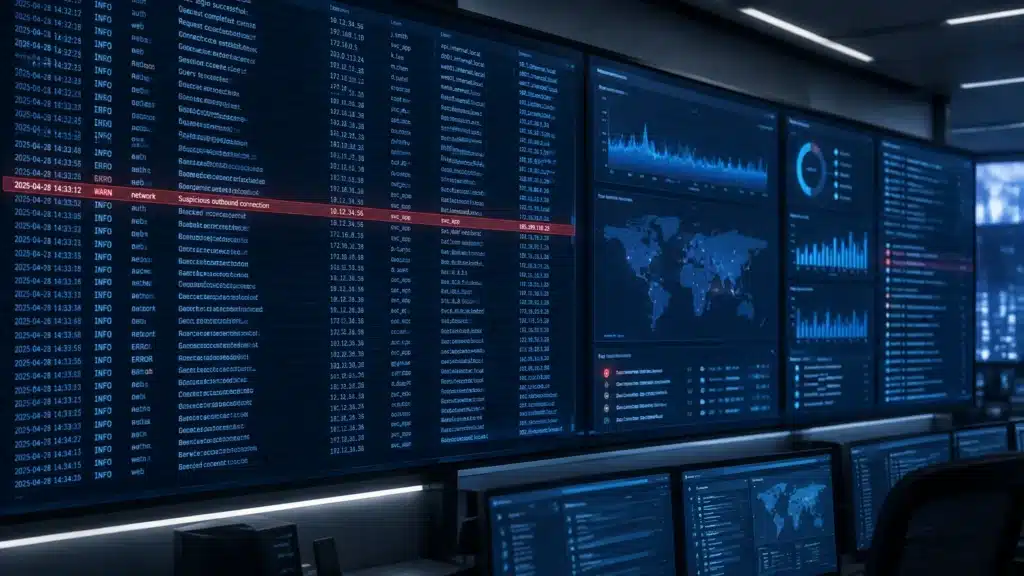
Your SIEM Is Collecting Logs, Not Detecting Threats A SIEM can be an important part of a security program. But
Your CMMC Score Is Not Your Compliance: Why Defense Contractors Fail the Second Assessment A strong CMMC score can open
Documented vs. Managed: The HIPAA SRA Question OCR Is Asking That Most Organizations Can’t Answer A completed HIPAA Security Risk
94% of Ransomware Attacks Target Your Backups: The Immutability Question Every Board Should Be Asking Most organizations can answer one
$893M in AI Fraud: Why a Cloned Executive Voice Is Now Your Biggest Financial Control Gap A voice message arrives
Zero-Days Don’t Wait for Your Patch Cycle: What the Citrix NetScaler Attacks Reveal About 2026 Exposure Management A monthly vulnerability
The Proposed HIPAA Security Rule Is Coming: Why July 2027 Is Closer Than You Think The proposed HIPAA Security Rule
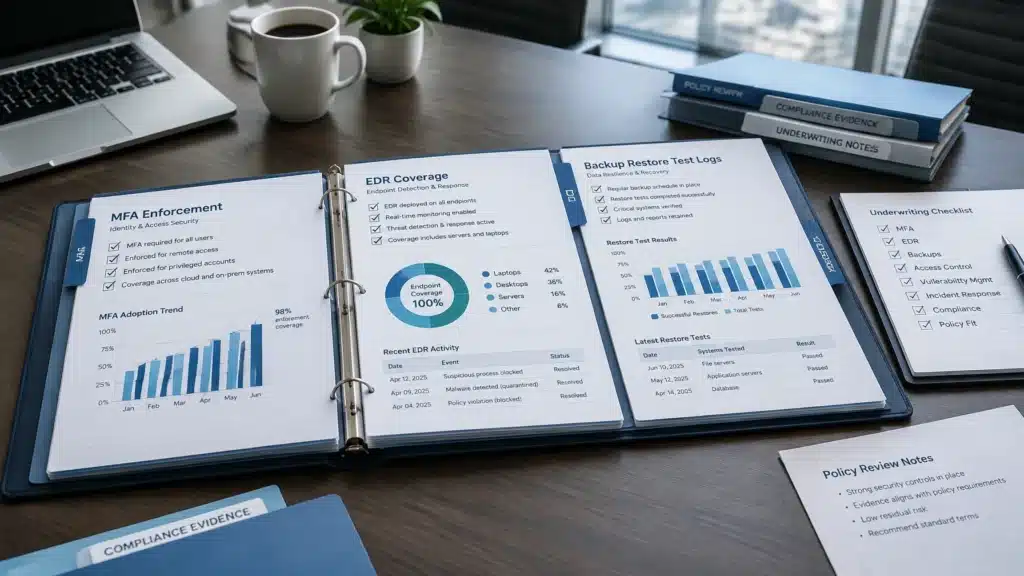
Cyber Insurers Want Evidence, Not Promises: Building the 2026 Proof Binder That Keeps Your Coverage Cyber insurance underwriting has changed.