Your Scan Report Won’t Save You: What HIPAA, Insurers, and CMMC Actually Want From Vulnerability Management
Your Scan Report Won’t Save You: What HIPAA, Insurers, and CMMC Actually Want From Vulnerability Management A vulnerability scan can […]

Your Scan Report Won’t Save You: What HIPAA, Insurers, and CMMC Actually Want From Vulnerability Management A vulnerability scan can […]
18% of Your IT Assets Aren’t Under Management: The Attack Surface You’re Not Watching You can’t patch what you can’t
1,746 CVEs Are Being Actively Exploited: Why ‘Patch Everything’ Fails and Risk-Based Prioritization Wins You cannot patch every vulnerability at
The #1 Breach Vector Just Changed for the First Time in 19 Years: Vulnerability Exploitation Overtook Stolen Credentials For the
65% of SMBs Now Outsource Security: The Seven Questions That Separate a Real SOC From a Dashboard Outsourcing security can
5 Billion Passkeys and Still Phishable: The MFA Fallback That Undoes Your Whole Rollout Five billion passkeys are now in
A $1.4M Penalty Became $140K: What a Dental Practice’s HIPAA Settlement Really Signals to Small Providers A $1.4 million proposed
A 2016 Flaw Still Works: Why Nation-State Attackers Keep Hitting Unpatched Systems A vulnerability disclosed a decade ago can still
You’re Only Logging 30% of What Matters: The Telemetry Gap That Blinds Your SOC Most organizations do not have a
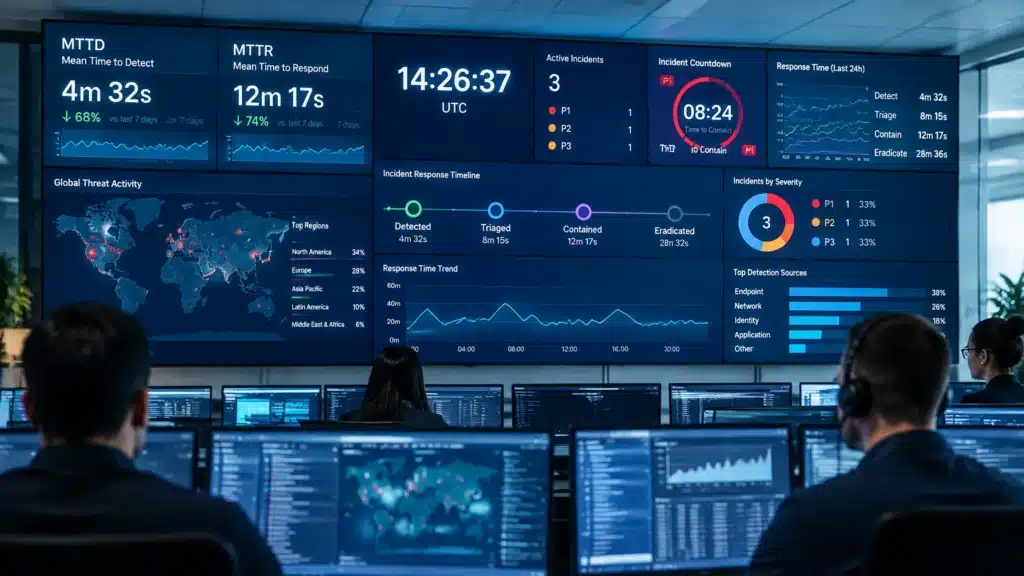
1,000 Alerts a Day, Zero Answers: Why MTTD and MTTR Are the Only SOC Metrics That Matter If your SOC