VIRTUAL CISO (vCISO)
Executive Security Leadership – Without the Full Time CISO
Cenova Cyber’s vCISO services give your organization on-demand, executive-level security leadership – reducing cyber risk, meeting compliance requirements, and aligning security with business goals—at a fraction of what a full-time CISO costs.
What is a virtual CISO (vCISO)?
A virtual CISO is an experienced security executive who leads your cybersecurity program on a part-time or on-demand basis instead of as a full-time hire. A vCISO sets strategy, manages risk and compliance, reports to leadership and the board, and is accountable for security decisions, typically for a fraction of a full-time CISO’s cost.
How a Cenova vCISO engagement works
- Assess — review your current security program, risks and compliance gaps.
- Plan — build a risk-based roadmap and budget aligned with business goals.
- Lead — own governance, policies and executive and board reporting.
- Execute — work alongside your IT team or provider to deliver the roadmap.
- Improve — quarterly reviews and annual strategic planning keep the program on track.
Compliance is more than a checklist — it’s a strategic function that protects your organization, supports business goals, and strengthens long‑term resilience.
At Cenova Cyber, we’ve spent decades seeing one challenge repeatedly: a widening gap between technical teams and organizational leadership.
A Chief Information Security Officer (CISO) is meant to bridge that gap — aligning cybersecurity, compliance, and business strategy. But not every organization needs (or can justify) a full‑time CISO.
That’s why more businesses are turning to Virtual CISO (vCISO) services: on-demand, executive-level cybersecurity leadership through a single, accountable point of contact.
Who Our vCISO Services Are Designed For
- Organizations with 50–1,000 employees
- Companies facing insurance, regulatory, or customer security pressure
- IT teams without dedicated security leadership
- Leadership teams that want clear accountability for cyber risk
SEE IF A VCISO IS RIGHT FOR YOU
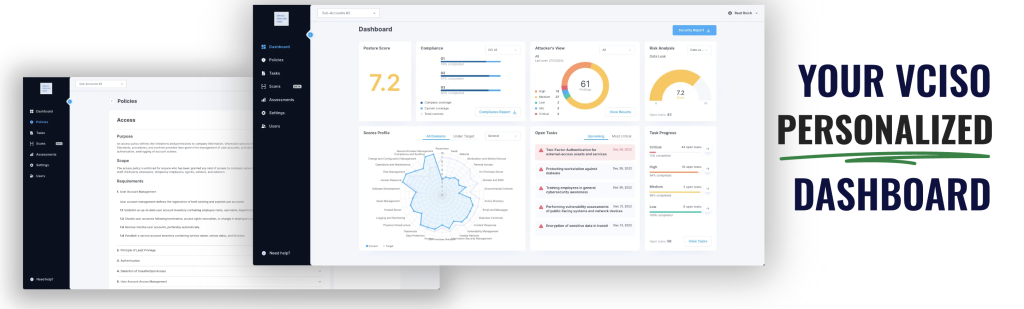
Why Organizations Choose a vCISO
Organizations today need practical solutions for managing risk, scaling security maturity, and meeting growing compliance obligations — especially when skilled security professionals are hard to find.
Our vCISO team delivers:
- Executive‑level cybersecurity leadership
- Multi‑disciplinary expertise across industries
- Support that fits your budget
- Compliance alignment built on national frameworks
We work with the standards your industry depends on, including: CMMC, HIPAA, CJIS, PCI, SOC 2, FFIEC, ISO 27001, HITRUST, NIST, CIS, FISMA, GDPR, and NERC‑CIP.
Closing the Gap Between Technical Teams and Leadership
Cybersecurity today is complex. Without experienced guidance, significant risks often go unnoticed — especially when organizations assign security responsibilities to someone without the executive‑level insight to manage enterprise risk.
A vCISO serves as a senior member of your leadership team, working alongside your CTO, COO, or CIO to:
- Establish cybersecurity strategy and governance
- Ensure compliance obligations are met
- Align security priorities with budget and business goals
- Provide tactical and strategic guidance
- Protect data, technology, and information assets
This is not a technician filling a role — it’s true security leadership.
Our vCISO Focus Areas
Our vCISO services provide both strategic direction and operational execution, ensuring your organization has a mature, well‑managed security program.
Compliance & Risk
- Compliance program management (CMMC, HIPAA, SOC 2, ISO 27001, and more)
- Security risk assessments and self-assessments
- Risk management, mitigation, and reduction strategies
- Cybersecurity strategy and program roadmaps
- Policy development, review, and management
- Board and executive-level risk reporting
Operational Security
- Incident response planning and tabletop exercises
- Security testing, validation, and remediation oversight
- Secure systems architecture and SDLC guidance
People & Process
- Decision support for leadership
- Security awareness training content and delivery
What This Means for You
With Cenova Cyber as your vCISO, you gain:
- A clear cybersecurity roadmap executives can understand
- Measurable risk reduction tied to business priorities
- Confidence during audits, insurance renewals, and customer reviews
- A single accountable leader for cybersecurity decisions
OUR VCISO STRATEGY
Cenova’s vCISO services bring true executive‑level leadership to your organization. Our team has decades of program‑building experience and deep compliance expertise, ensuring your security program is aligned, measurable, and effective. Our strategy is to use a risk-based approach, balancing the cybersecurity, compliance and business needs. Working with your organization to support the rate of change best suited for the business and people.
Whether you need fractional leadership, additional expertise, or temporary executive support, our vCISO services scale to your needs and budget.
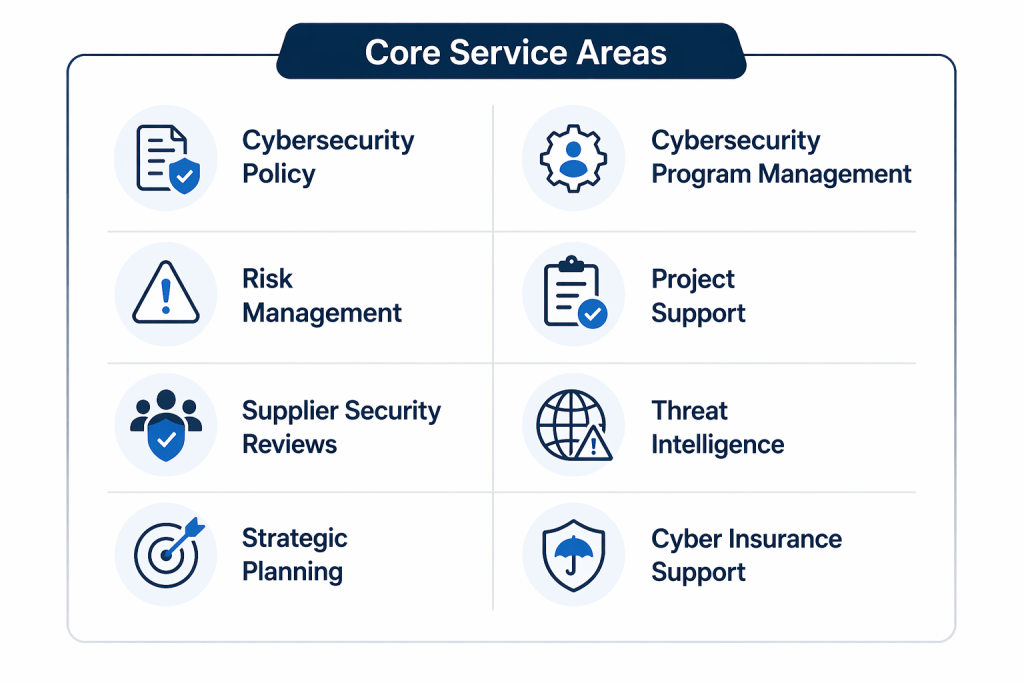
What Our vCISOs Support
- Policy Development, Review & Management
- Cybersecurity Program Development
- Security Risk Assessments
- Risk Management & Reporting
- Security Testing & Validation
- Remediation Oversight
- Decision Support for Leadership
- SDLC & Secure Architecture Guidance
- Incident Response Planning
- Training Content & Delivery
- Self‑Assessments
- Secure Systems Architecture
- Risk Mitigation & Reduction Strategies
- Compliance Management
Why Choose Cenova’s vCISO Services?
- Access to an entire team of experts
- Cost‑effective compared to hiring full‑time staff
- Knowledge of all major compliance standards
- Scalable and flexible to your business needs
- Experience across multiple industries and environments
- Objective, independent guidance
- Lessons learned from supporting diverse organizations
FLEXIBLE VCISO PACKAGES FOR ANY LEVEL OF SUPPORT
Cenova will tailor a vCISO package to your organization’s specific needs — with flexible pricing and responsive support through email, phone, and direct messaging.
Whether you need occasional advisory help or ongoing executive leadership, our vCISO services deliver the cybersecurity expertise required to protect your business.
Pricing & Packages
A full-time CISO typically costs $185,000–$250,000+ per year in salary alone, before benefits, bonus, and recruiting costs. Cenova’s vCISO plans start at $4,500/month — a fraction of that investment, with a full team behind every engagement.
Advisory
Best for organizations that need periodic strategic guidance and compliance check-ins. Starting at $4,500/month.
Standard
Best for organizations actively building a security program or working toward a compliance deadline. Starting at $9,800/month.
Executive
Best for organizations that need a vCISO embedded in leadership meetings and ongoing program ownership. Starting at $14,800/month.
Free Guides & Checklists
Free resources from the Cenova Cyber team for leaders building or improving a security program.
The vCISO Buyer’s Guide
What a virtual CISO does, when your business needs one and what to look for in a provider.
Incident Response Tabletop Exercise Scenarios
Three realistic scenarios your leadership team can run to pressure-test your incident response plan.
Frequently Asked Questions
Q1. How is a vCISO different from a security consultant?
A consultant typically delivers a project and moves on. A vCISO is an ongoing, accountable member of your leadership team — responsible for your security strategy, not just a single deliverable.
Q2. How much time will this take from my team?
This depends on where your organization is with your security program and how complex your needs are. Typically, there is an onboarding period, similar to any new team member. We utilize a documentation system which facilitates information sharing among our team. Most clients meet with their vCISO for 2-5 hours per month, with additional availability by email and phone as issues come up.
Q3. How quickly can we get started?
Most engagements kick off within one to two weeks of signing. Our vCISOs are deliverable-based and not hours-based. We start with a plan and work through that plan as the program matures, adjusting the plan as necessary.
Q4. How much does a vCISO cost?
Cenova’s vCISO plans start at $4,500 per month for Advisory, $9,800 for Standard and $14,800 for Executive, compared with $185,000 to $250,000 or more per year in salary alone for a full-time CISO.
Q5. Do we need a vCISO if we already have an IT provider?
Often, yes. An IT provider keeps systems running, while a vCISO owns security strategy, risk, compliance and leadership reporting. The two work together, and your vCISO can hold your IT provider to a clear security roadmap.
Get a free consultation
Find out if a vCISO is right for your organization, with no obligation.
Prefer to talk? Call (844) 236-6820 (844-CENOVA0).