Your Firewall Doesn’t Matter Anymore: Identity Is the Control Plane Attackers Actually Fight Over
A firewall still has a job. It can help control network traffic and reduce exposure. But it can’t decide whether a signed-in user should access payroll, whether an application can read company email, or whether a stolen session should retain access to sensitive data.
Those decisions now depend on identity.
Employees, contractors, administrators, service accounts, applications, and cloud workloads all use identities to access business systems. Identity systems determine who or what can authenticate, what that identity can reach, and which actions it can perform. That makes identity a practical control plane for modern security.
Attackers know it. They often don’t need to break through a network boundary if they can sign in using credentials, tokens, or permissions that already work.
THE PERIMETER HAS CHANGED
Business access no longer begins and ends at the office network. Employees use cloud applications, email, file sharing, remote access, and mobile devices from many locations. Partners and vendors may need access too. Applications and automated services connect to systems without a person sitting at a keyboard.
A network firewall remains one useful security layer, but it can’t make every access decision in this environment. Identity controls help determine whether a request should be allowed based on who or what is requesting access, the resource involved, and relevant conditions such as device posture or sign-in risk.
This is why identity sits at the center of a broader security program. Endpoint protection, email security, and network controls all matter. But when access is granted to an account with excessive permissions, or when an attacker takes over an identity, those other defenses may have less room to prevent harm.
WHY ATTACKERS GO AFTER ACCESS
For many attackers, stealing or manipulating access can be a more direct route than exploiting a technical vulnerability. They may phish a password, persuade a support team to reset an account, steal a session token, or convince a user to approve an application.
With valid access, activity can resemble normal work. A compromised user may sign in to email, search files, or access business applications using ordinary tools. That doesn’t mean endpoint detection and response (EDR) is useless; it means identity and behavior signals are essential context for investigating suspicious activity.
A successful login is not proof that the person or application behind it is trustworthy. Defenders need to ask: Does this identity need this access, and does this activity make sense?
> The help desk post earlier this week covered one possible entry point: social engineering a password reset. The broader lesson is that preventing a single reset scam is not enough. Organizations also need governance for what identities can access, and monitoring for how that access is used.
THE IDENTITY ATTACK SURFACE IS LARGER THAN EMPLOYEE ACCOUNTS
A useful identity review looks beyond the list of active employees. It considers the full collection of accounts, credentials, grants, and trust relationships that can open a path to business systems.
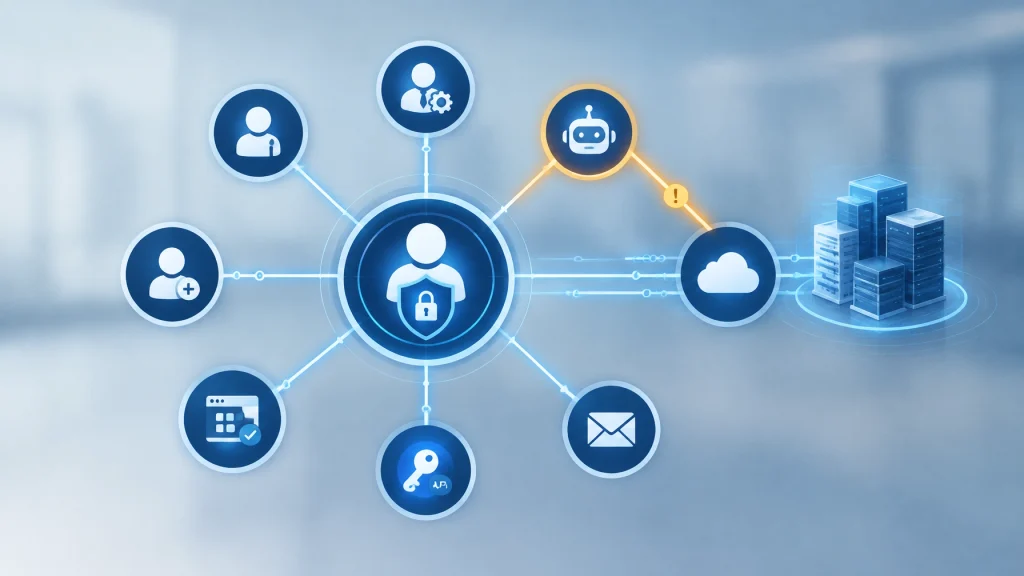
- Primary accounts give employees access to email, collaboration tools, cloud platforms, and other services.
- Privileged accounts can administer systems, change policies, or access sensitive data. Their permissions make them especially important to protect.
- Service accounts and workload identities allow applications, scripts, and automated processes to connect to systems. They may operate continuously and can be overlooked if no one owns their access.
- Break-glass accounts provide emergency access when normal authentication or administration is unavailable. They are useful only when tightly controlled, protected, and tested.
- API keys, secrets, and certificates allow software or integrations to authenticate. If they are exposed, untracked, or left active after they are no longer needed, they can create persistent access paths.
- OAuth grants and application consents authorize applications to access data or act on behalf of users. An approved-looking sign-in does not automatically make an app’s permissions appropriate.
- Guest accounts provide external users with access to internal resources. Access that outlives a project or relationship can become an avoidable risk.
- Federated identity trusts connect identity environments. A trust can simplify access across organizations, but it also makes clear ownership and monitoring important.
- The SSO provider centralizes authentication for many services. That can make access easier to manage, but it also makes the provider a high-value security dependency. Protect its administrators, recovery processes, integrations, and emergency accounts accordingly.
No single checklist can replace understanding how your environment works. Start by finding the identities and access paths that matter most to your operations and sensitive data.
BUILD AN IDENTITY HYGIENE BASELINE
Identity security is not a one-time MFA rollout. It is a set of controls that work together to reduce unnecessary access, make authentication harder to steal, and surface misuse sooner.
1. Strengthen authentication
Require MFA for business accounts and prioritize phishing-resistant methods where the service supports them. The CISA guidance on implementing phishing-resistant MFA explains why not all MFA methods resist the same attacks and identifies phishing-resistant authentication as the strongest option.
Plan for the full authentication lifecycle, not just sign-in. Enrollment, account recovery, help desk resets, and lost-device procedures need safeguards too.
2. Use conditional access
Apply access policies that consider more than a correct password. Depending on your identity platform and business requirements, conditional access can factor in the application, account role, device state, location, or risk signals. Use it to restrict access to sensitive resources and set stronger requirements for privileged activity.
3. Keep permissions narrow and review them
Grant only the access required for a person or service to do its job. Separate everyday user accounts from administrative accounts where practical, and use time-limited elevation for sensitive tasks when your tools support it.
Review privileged roles, group membership, guest access, and application permissions regularly. Remove access when responsibilities change, accounts become inactive, or a project ends.
4. Inventory service accounts and credentials
Identify service accounts, workload identities, API keys, secrets, and certificates. Document their owners, purpose, permissions, and renewal or retirement process. Where supported, prefer managed identity options over long-lived credentials that require manual storage and rotation.
5. Govern OAuth consent and app access
Decide who can approve applications and which permissions require administrator review. Remove unused grants and investigate unexpected consent or permission changes. An application’s access should be treated as a security decision, not simply an end-user convenience.
6. Monitor privileged operations and identity changes
Watch for unusual sign-ins and changes to accounts, MFA methods, devices, permissions, application grants, and credentials. Pay particular attention to activity that changes who has administrative access or creates a new route into business data.
GOVERNANCE AND MONITORING MUST WORK TOGETHER
Good policies establish what access should look like. Monitoring helps identify when reality diverges from those policies.
For example, a new application may request access to sensitive data, an administrative account may be used in an unusual way, or a service identity may begin accessing a resource outside its normal role. Each event needs context. A single alert may be benign; a pattern of identity, endpoint, and cloud activity may indicate a serious issue.
A 2026 Microsoft overview of identity security also describes the challenge of fragmented identity and security signals, and emphasizes the importance of understanding what identities can access, not only who they are.
For organizations without a dedicated identity security team, that work can be difficult to sustain alongside daily IT responsibilities. The goal is not to collect every possible alert. It is to establish clear ownership, meaningful policies, and a process to investigate and respond to suspicious access.
MAKE IDENTITY PART OF YOUR SECURITY STRATEGY
Identity security touches technical configuration, business processes, and accountability. A vCISO can help leadership prioritize risk, define governance, and build an identity roadmap that fits the organization. A managed security team can help monitor relevant security signals and investigate suspicious activity.
Cenova Cyber provides managed cybersecurity services with ongoing security operations and monitoring, as well as vCISO services for risk-based strategy, governance, and program leadership.
Request an identity security review. We can help you identify high-impact accounts and access paths, assess your current controls, and prioritize practical next steps. Contact Cenova Cyber to start the conversation.