Two PHP Zero-Days and an Exploited Edge Appliance: Why Web-Facing Infrastructure Keeps Paying Attackers
Web-facing systems connect customers, employees, cloud services, and internal applications. That reach makes them essential to daily operations, and attractive to attackers. Two critical PHP remote code execution vulnerabilities and an actively exploited SQL injection flaw in on-premises VeloCloud Orchestrator put that exposure into sharp focus.
The immediate priority is to find affected systems, confirm patch status, and look for signs of compromise. But it is important to distinguish the threats: the PHP vulnerabilities allow unauthenticated remote code execution; the VeloCloud Orchestrator flaw requires an authenticated portal session. Both need urgent attention, but they do not have the same attack prerequisites.
PHP: A PUBLIC WEB REQUEST CAN BECOME CODE EXECUTION
CISA’s urgent PHP alert covers CVE-2026-109618 and CVE-2026-109619, collectively referred to as “php2shell.” The vulnerabilities can allow an unauthenticated attacker to execute code against PHP installations serving web requests. A web application does not need to contain a separate application-level flaw for the vulnerable PHP runtime to be at risk.
Affected setups include Apache with mod_php, PHP-FPM, php-cgi, FrankenPHP, and LiteSpeed. CISA identifies mod_php as the highest-risk configuration. The PHP project has released fixed versions: 8.5.12, 8.4.27, 8.3.36, and 8.2.35. Organizations running older versions should check with their operating-system or software vendor for supported backported fixes. A version string alone may not tell the whole story if a vendor has applied a backport.
CISA said it had not observed successful exploitation of these PHP vulnerabilities in the wild when its alert was published. That is not a reason to wait. CISA urges organizations to inventory PHP, patch immediately, prioritizing internet-facing systems, and monitor for suspicious activity.
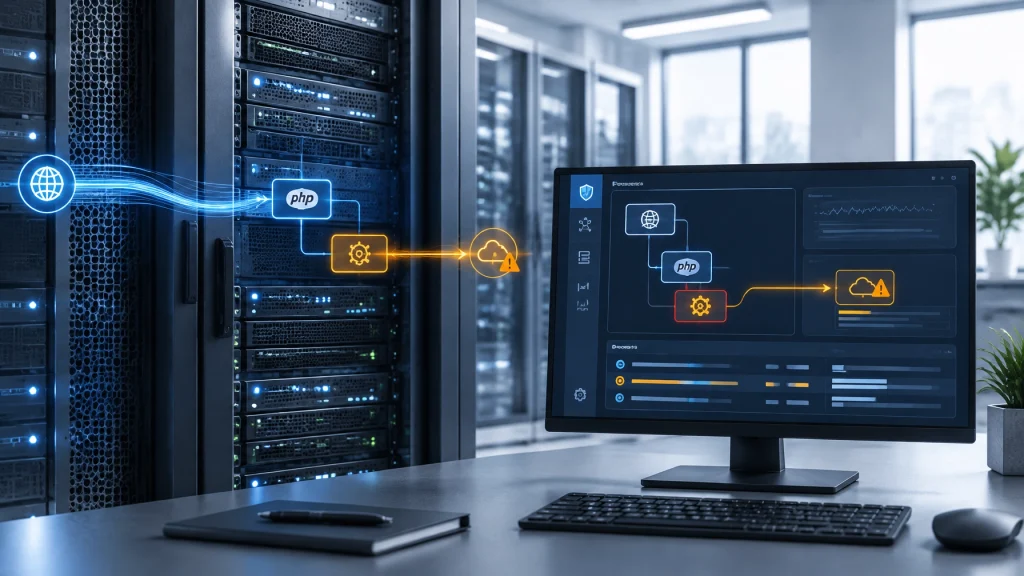
An exposed web server can also provide a route deeper into the organization. If an attacker gains code execution under a web-service account, they may try to access application secrets, read accessible files, probe internal systems, or establish a foothold for further activity. The level of access depends on the server’s configuration and permissions, but a public-facing server should not be treated as isolated by default.
VELOCLOUD ORCHESTRATOR: A DIFFERENT ATTACK PATH, AN URGENT PATCH
CVE-2026-114625 is a SQL injection vulnerability in on-premises VeloCloud Orchestrator (VCO). Arista says it is being actively exploited, and CISA added it to the Known Exploited Vulnerabilities catalog.
There is an important detail for assessing risk: this specific flaw requires network access to the VCO web interface and a valid authenticated portal session. Arista reports that even the lowest built-in tenant role, Enterprise Read Only, can be sufficient to gain operator privileges and access privileged internal functionality. So, while the PHP issues allow unauthenticated RCE, the VCO vulnerability is not described by Arista as pre-authentication.
Affected on-premises VCO releases should be upgraded to fixed versions: 5.2.3.18 or later, 6.1.3.10 or later, and 6.4.2.12 or later in their respective release trains. Arista says hosted, including dedicated, VCO versions have already been patched. Organizations that cannot upgrade immediately should restrict access to trusted administrative networks, review administrator activity, monitor for unexpected outbound connections, and look for webshells or backdoor processes. These are interim defenses, not a replacement for upgrading.
The issue matters because orchestration and edge infrastructure sit at a strategic junction. These systems help connect remote workers, branch offices, and business networks. A compromise could put management functions and connected environments at risk. Confirm whether your organization operates on-premises VCO; don’t assume that every VeloCloud or Arista product is affected. Use the Arista advisory to check product and software applicability.
FOUR EXPOSURE QUESTIONS TO ANSWER NOW
Start with an inventory, not an assumption that the systems you know about are the only ones in use. PHP can be embedded in third-party products, hosted applications, and systems managed by a vendor or business unit.
Ask:
- Do we run PHP anywhere internet-facing? Include public websites, APIs, customer portals, staging environments, and PHP components bundled with other software.
- Which PHP versions and deployment modes are in use? Identify the host, service owner, exposure, and whether a fixed release or verified vendor backport is installed.
- Do we operate or resell on-premises VeloCloud Orchestrator? Identify the VCO release, whether the management interface is reachable from untrusted networks, and who has portal access.
- What is the patch and compromise status of each system? Record when it was patched, whether suspicious activity has been reviewed, and who owns any remaining remediation.
If a PHP-based system cannot be updated promptly, CISA advises taking it offline until it can be patched or updated. A web application firewall may offer some protection during a short transition, but it does not fix the underlying vulnerability. PHP’s security release guidance also describes temporary measures for specific attack paths; the PHP team emphasizes that these do not make an installation safe. Treat them as risk reduction while arranging the update, not as a substitute for it.
PATCHING IS ONLY HALF THE RESPONSE
Remote code execution can leave evidence beyond the original web request. Look for unexpected PHP files, especially in web-accessible or upload directories; new or modified scripts; unusual processes launched by PHP or the web-server account; and outbound connections that do not fit the server’s normal role. A process such as a shell, downloader, or reconnaissance utility spawning from a web worker deserves investigation.
Basic availability monitoring or a routine vulnerability scan may not reveal these behaviors. Endpoint telemetry can show process lineage (what launched what, under which account) and help connect a suspicious process to a file change or network connection. File-integrity monitoring, web-access logs, and outbound network records add further context.
For VCO, review the web-access, application, system, and administrator activity logs. Arista recommends preserving relevant logs and file-system timestamps before remediation when compromise is suspected and it is operationally feasible. That evidence can help establish what happened and whether additional response steps are needed.
MITRE ATT&CK’s web-shell detection guidance describes useful detection patterns, including unauthorized script files followed by unexpected commands launched by a web server. The key is to correlate signals: a new file on its own may be benign; an unexpected file followed by process creation and outbound traffic is much harder to dismiss.
DISCOVER, PATCH, MONITOR, VERIFY
A focused response brings exposure management and security monitoring together:
- Discover: Find PHP deployments and on-premises VCO systems, including assets managed by other teams or providers.
- Prioritize: Put internet-facing vulnerable PHP and affected VCO deployments at the front of the remediation queue.
- Patch: Apply fixed releases or confirm a supported vendor backport. Restrict access or take a vulnerable system offline if immediate patching is not possible.
- Monitor: Watch web servers for suspicious files, process behavior, and outbound connections; review VCO access and administrator activity.
- Verify: Confirm the installed fix, rescan or recheck the asset, and investigate signs of activity that may have occurred before remediation.
Cenova Cyber’s Vulnerability Management as a Service supports asset discovery, risk-based prioritization, remediation tracking, and verification. Our 24/7 security monitoring and SOC helps investigate suspicious endpoint and system activity, including behavior that a basic scan will not detect.
GET A FREE EXPOSURE CHECK
Don’t wait for a routine scan cycle to find out whether a vulnerable web server or management interface is exposed. Contact Cenova Cyber for a free exposure check. We’ll help identify the systems to review, clarify patch status, and discuss what monitoring can help detect if an attacker has already tried to get in.