The Claim Denial Arrives After the Breach: Why Restore Test Logs Decide Whether Your Insurance Pays
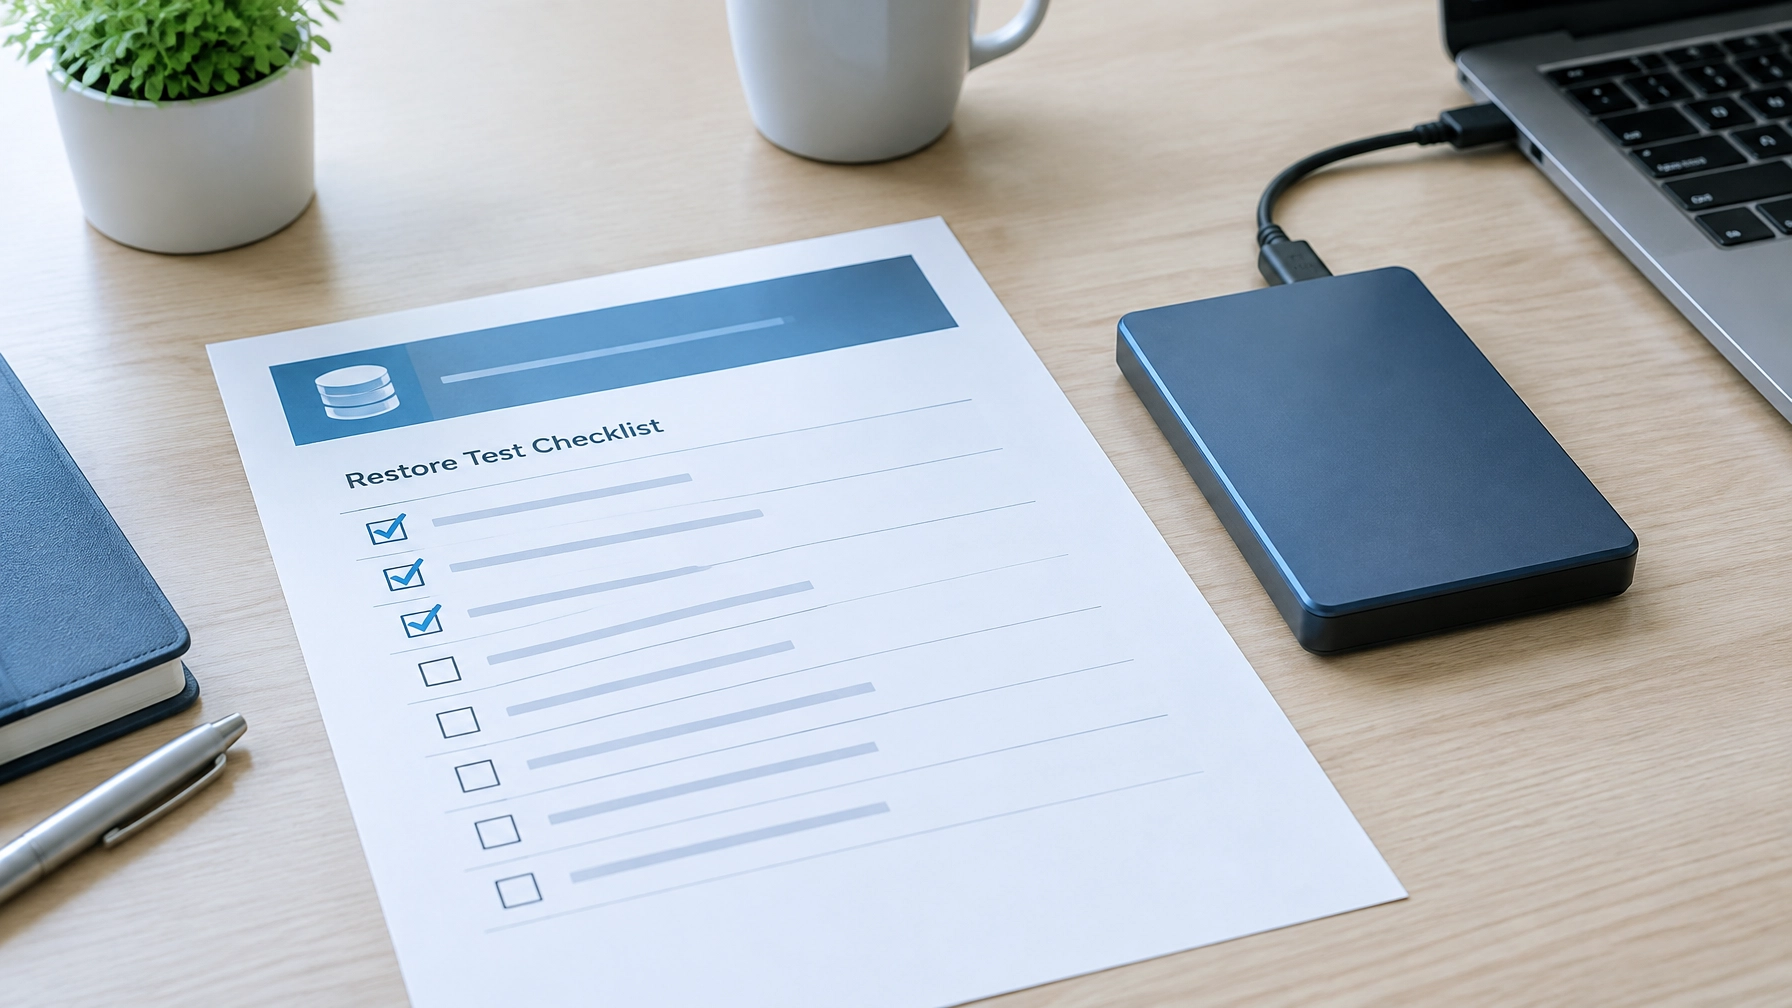
A backup job marked “successful” is not proof that your business can recover. It shows that a process ran, not that the right systems and data can be restored, that the restored information is usable, or that recovery can meet your business’s documented time objectives.
That distinction matters when a ransomware claim is under review. Insurers may compare the controls described in your application with the controls that were actually in place when the incident occurred. If you attested that backups were protected and regularly tested, dated records of successful restore tests can help show what that meant in practice.
Without those records, your organization may face two problems at once: uncertainty about recovery and a difficult question about what it represented to its insurer.
A BACKUP IS NOT THE SAME AS A SUCCESSFUL RESTORE
Backups are essential, but backup frequency alone cannot tell you whether recovery will work. The copy could be incomplete, inaccessible, corrupted, too old, or exposed to the same compromised credentials and network as production systems.
The Cybersecurity and Infrastructure Security Agency (CISA) recommends scheduled recovery tests to verify backup integrity and help refine recovery point objectives (RPOs) and recovery time objectives (RTOs). CISA also advises organizations to test full and partial restoration and to know how to access critical files without an internet connection. Read CISA’s backup guidance.
The National Institute of Standards and Technology (NIST) likewise includes periodically tested backups in its data-integrity guidance. Its ransomware recovery example uses logs and file integrity information to identify a last-known-good point, restore affected files, and confirm the recovery result. See NIST SP 1800-11.
A restore test turns a backup assumption into an operational result. It asks whether the right people can retrieve the right data, using the actual recovery method, in a timeframe the business can accept.
THE ATTESTATION-TO-AUDIT LIFECYCLE
Cyber insurance applications often ask about specific security practices. Those answers may become representations the insurer relies on when evaluating risk. If a claim follows, the insurer may review application answers alongside technical records, policy requirements, incident evidence, and the scope of affected systems.
The important discipline is not to give the answer that sounds best. It is to make sure each answer reflects what is implemented, and what can be demonstrated, on the relevant date. Be precise about scope. “MFA is enabled for remote access” means little if some remote access paths are excluded. “Backups are tested” should correspond to actual tests and retained records.
A publicly available example illustrates why accuracy matters. In Travelers v. International Control Services, the parties stipulated to rescission of a policy following a dispute about application representations, including MFA. The court order does not establish that every inaccurate answer automatically defeats coverage; it does show why organizations should take application statements seriously and retain evidence supporting them. Read the stipulated order.
This does not mean every control gap results in a denial. Coverage depends on the policy wording, application, facts, applicable law, and insurer’s analysis. Missing restore-test records can, however, make it harder to demonstrate that a stated control operated as represented, or to establish what recovery capability was available.
WHAT A DEFENSIBLE RESTORE TEST RECORD CONTAINS
A useful record should let another person understand what was tested, what happened, whether recovery objectives were met, and what the organization did about any problems. Keep supporting evidence, such as backup job reports, screenshots, logs, and service tickets, with the record, and store it securely.
RESTORE-TEST EVIDENCE CHECKLIST
- Date and scope: When the test occurred, and whether it was a file-level, partial, or full-system restore.
- System and data restored: Identify the server, application, database, or dataset. Note the backup version or recovery point used.
- Backup protection: Record whether the tested copy was immutable, offline, isolated, encrypted, or otherwise protected from production access.
- Method and conditions: Describe the restoration steps, tools, dependencies, and whether recovery took place in a clean or isolated environment.
- Elapsed time and objective: Capture start and end times, actual recovery duration, and the documented RTO. Include the relevant RPO or data-loss window where applicable.
- Validation result: Confirm that restored data was accessible, complete, and usable. Record how the team checked its integrity and business functionality.
- People involved: Name the person who performed the test and the person who witnessed or approved it.
- Issues and follow-up: Document failures, delays, missing dependencies, or other findings, plus the remediation owner, action taken, and retest result.
- Evidence retained: Attach relevant logs, screenshots, reports, change or incident tickets, and approvals. Preserve dates and context.
A test that finds a problem is still valuable, if the problem is documented and addressed. A failed restore hidden in a help-desk ticket is not a reliable recovery record. A failed restore followed by an assigned corrective action and a passing retest shows an organization working to close the gap.
OTHER CONTROL GAPS CAN COMPLICATE A CLAIM
Backup evidence is one part of a larger security picture. Insurers may also look at whether controls described in an application applied to the systems involved in the incident. Common areas to review include:
- MFA coverage: Confirm that remote access and privileged accounts are covered as represented. Maintain configuration exports, exception records, and relevant identity logs.
- Known-exploited vulnerabilities: Keep an asset inventory, vulnerability findings, patch records, and documented decisions for systems that cannot be patched promptly. Cenova Cyber’s VMaaS supports ongoing discovery, risk-based prioritization, remediation tracking, and validation reporting.
- EDR coverage: Retain records showing which endpoints were protected, whether agents were healthy, and how alerts were investigated. CISA advises organizations responding to ransomware to examine endpoint detection and prevention systems and related logs. See CISA’s ransomware response guidance.
None of these controls guarantees claim payment, and an individual gap does not automatically determine coverage. The goal is to understand what the policy and application require, maintain controls across the stated scope, and preserve evidence of exceptions and remediation.
BUILD THE RECORD BEFORE YOU NEED IT
Set a restore-test cadence based on business risk, recovery objectives, and policy requirements. Test critical systems, not just a convenient sample, and include the people responsible for technical recovery and business validation. If a test misses the RTO or reveals unusable data, assign corrective action and retest.
Review cyber-insurance applications before renewal with the people who know how controls are configured. Compare each answer with current system coverage, logs, exception lists, and test records. If a control is not fully implemented, document the gap and create a remediation plan rather than overstating the answer.
Cenova Cyber helps organizations strengthen this discipline through 24/7 security monitoring, VMaaS for vulnerability and patch evidence, and vCISO support for insurance-readiness documentation, risk oversight, and security program planning. Explore security monitoring and vCISO services.
TURN BACKUP CLAIMS INTO TESTED EVIDENCE
Nightly backup logs can show that copies were created. A dated restore-test record shows whether the organization could use those copies, and how long recovery took. That evidence supports a clearer view of operational readiness and helps align insurance representations with what your team can prove.
Contact Cenova Cyber for an insurance readiness review. We’ll help you examine backup restore evidence, control coverage, and documentation gaps before renewal, not after a breach puts them under scrutiny. Schedule a free security consultation.
This article provides general information, not legal or insurance advice. Coverage depends on the policy, application, facts, and applicable law. Review specific questions with your insurance broker, carrier, and legal counsel.