When Your Lab Platform Is Breached: The Quest Diagnostics Attack and the Vendor Question Every Practice Must Answer
A laboratory-ordering platform is more than a place to submit test requests. It is part of the clinical workflow: connecting providers, patient information, and diagnostic services. When access is disrupted or patient data is exposed, the effects can reach beyond the vendor’s systems.
Quest Diagnostics’ late-October 2026 notice about unauthorized access to its Quanum Lab Services Manager (LSM) platform is a timely reminder for every healthcare organization: your vendor’s incident can create operational, privacy, and compliance work for your practice.
WHAT QUEST HAS REPORTED
Quest said it identified unauthorized access to Quanum LSM, which certain clients use to place test orders and receive or look up results. In its incident notice and provider FAQs, Quest said it believed some patient data was accessed and confirmed that PHI and personally identifiable information were involved. The investigation was ongoing, and Quest had not yet identified the specific data or patients affected.
Quest also said its core business operations remained up and running. Providers using direct customer laboratory information system (LIS) interfaces or electronic medical records (EMRs) could continue ordering through those channels. For Quanum LSM users, Quest described alternatives including paper requisitions and Quanum eLabs.
Those details matter. Do not assume a reported platform incident means every connected system was affected, or that every practice experienced the same operational impact. Confirm what applies to your organization, its records, and its workflow directly with the vendor.
Even when the laboratory continues operating, a disruption to the ordering path can create extra steps for staff. A practice may need to verify orders through alternate channels, track pending results, and make sure clinicians receive information they need for care decisions. That is why incident planning must cover clinical continuity as well as technical containment.
YOUR VENDOR’S PLATFORM IS PART OF YOUR RISK PICTURE
Healthcare organizations rely on specialized platforms for laboratory orders, imaging, billing, patient communications, and practice management. These tools can improve access and efficiency, but they also create dependencies. A vendor platform may store or transmit PHI, connect to your EHR, or support a workflow that becomes difficult to replace quickly.
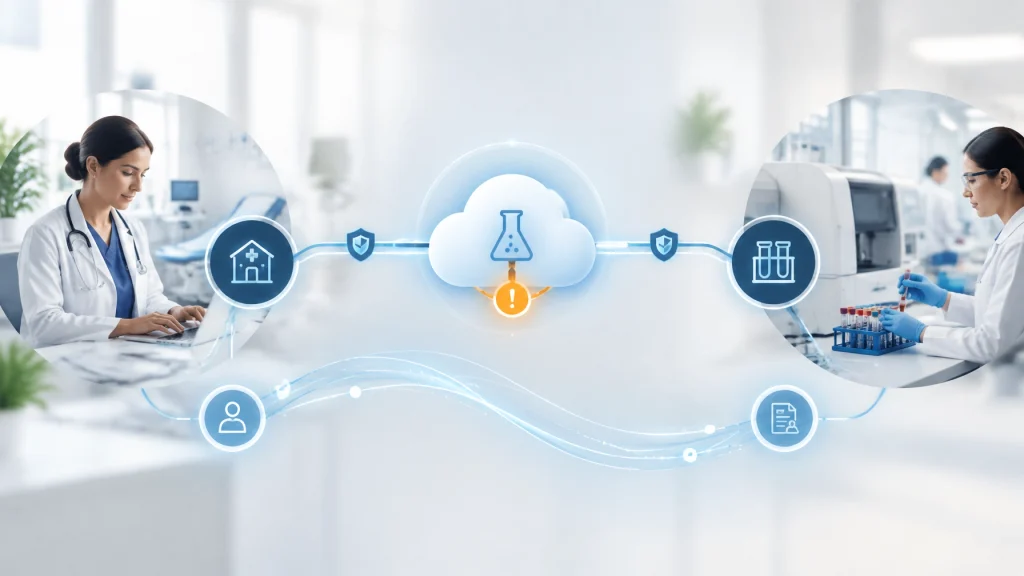
Before an incident, map those dependencies:
- What PHI does the platform receive, store, or transmit?
- Which systems and workflows connect to it?
- Who owns the clinical or administrative workaround if it is unavailable?
- How will the vendor notify you, and what information must it provide?
- What evidence will you need to assess risk and make decisions?
A signed business associate agreement (BAA) is essential when the vendor is acting as your business associate and handles PHI on your behalf. But the BAA is not a substitute for operational readiness, monitoring, or a clear response process. Confirm the vendor’s role and the agreement’s terms for the specific service and data involved.
A VENDOR’S BREACH DOES NOT AUTOMATICALLY CLOSE YOUR HIPAA RESPONSIBILITIES
HIPAA assigns obligations to business associates as well as covered entities. Under the Breach Notification Rule, a business associate that discovers a breach of unsecured PHI must notify the covered entity without unreasonable delay and no later than 60 calendar days after discovery. A BAA may require faster notice and more detail, so the regulatory maximum should not be treated as your response target.
The covered entity has its own duties. When a breach involves PHI for which the covered entity is responsible, it must assess the situation, determine whether notification is required, and meet applicable deadlines. Individual notices generally must be sent without unreasonable delay and no later than 60 calendar days after discovery. Depending on the incident’s scope, reporting to HHS and notice to prominent media may also apply. See the HHS Breach Notification Rule and 45 C.F.R. § 164.404.
The vendor’s investigation can help establish the facts, but your organization should not assume that the vendor’s notification or patient communications automatically satisfy every obligation that may apply to your practice. Clarify who is responsible for each notice under the facts and the contracts. Involve your privacy officer, legal counsel, and incident response team as appropriate.
Document the risk assessment and the basis for your decisions, including what information was affected, what is still unknown, how you evaluated likely impact, and what steps you took to mitigate harm. Preserve the timeline and supporting evidence. These records help your organization explain its actions if regulators, patients, insurers, or business partners ask questions later.
BUSINESS ASSOCIATES CAN FACE DIRECT ENFORCEMENT
Business associates are directly liable under HIPAA for certain requirements made applicable to them through the HITECH Act and implementing regulations. HHS explains the scope in its Business Associate Direct Liability fact sheet.
OCR enforcement actions demonstrate that a vendor can be an enforcement target, not just the healthcare provider that hired it. For example, OCR has resolved cases involving business associates after ransomware or other security failures, including actions against Comstar and BST & Co. CPAs.
Covered entities also cannot ignore known material problems with a business associate. Under 45 C.F.R. § 164.504(e), when a covered entity knows of a business associate’s material breach or violation of its agreement, it must take reasonable steps to cure the issue or end the violation. If those steps are unsuccessful, the covered entity generally must terminate the agreement if feasible. A breach does not mean a covered entity is automatically liable for every independent act of its vendor, but a known issue requires a considered response.
A PRACTICAL VENDOR INCIDENT CHECKLIST
When a vendor reports a security incident, act promptly and keep the work coordinated. Assign an incident lead and track decisions as the facts develop.
- Confirm what data was involved. Ask which systems, records, and data elements may have been accessed or affected. Request an explanation of what is confirmed, what remains under investigation, and when the vendor expects to provide updates.
- Get the timeline in writing. Record when the incident began, when it was discovered, when the vendor contained it, when your organization was notified, and when relevant services were restored or alternative workflows became available.
- Check your own environment. Confirm whether your systems, accounts, integrations, or user credentials were involved, and whether the vendor’s incident could have originated through your environment. Coordinate technical validation with your IT and security teams.
- Review notification duties and deadlines. Consult your BAA and incident-response plan. Identify who is responsible for which notifications, what information is required, and which legal or regulatory clocks may apply. Get legal guidance where needed.
- Document the assessment and response. Preserve vendor communications, system records, decisions, mitigation actions, and the rationale for your breach determination. Update the record as verified facts change.
- Review the BAA and vendor controls. Check incident-notice requirements, cooperation obligations, evidence access, subcontractor terms, and the process for addressing deficiencies. Track corrective actions through closure.
Also activate your clinical continuity plan. Identify how staff will place orders, receive results, escalate urgent cases, and reconcile work completed through alternate channels. A workaround should have clear ownership and a process for returning to normal operations.
TURN VENDOR OVERSIGHT INTO A REPEATABLE PRACTICE
Vendor risk governance works best before a breach. Maintain an inventory of services that handle PHI, document each service’s business purpose and system connections, and make sure contracts, risk assessments, and incident procedures reflect how the service is actually used. Test the response plan with the teams who would manage a real disruption: clinical operations, IT, privacy, compliance, and leadership.
Cenova Cyber helps healthcare organizations strengthen HIPAA risk management, security monitoring, incident response, and vendor oversight. Our HIPAA compliance services support risk assessments and practical remediation. Our vCISO services help leadership establish security governance and accountability for third-party risk.
Schedule a free HIPAA risk assessment consultation with Cenova Cyber. We’ll discuss your current vendor oversight and incident-response readiness, so you can identify gaps and take clear next steps. Request a HIPAA consultation.