
Your Scan Report Won’t Save You: What HIPAA, Insurers, and CMMC Actually Want From Vulnerability Management
A vulnerability scan can identify technical weaknesses. It cannot, by itself, show that your organization understood the risk, decided what to do, assigned responsibility, or verified the fix.
That distinction matters when an auditor, cyber insurer, or CMMC assessor asks how your vulnerability management program works. A report full of findings is only one artifact. The harder question is whether you can trace each relevant finding from discovery through risk decision and resolution, or explain why it remains open.
The goal is not to produce more scanning paperwork. It is to show a repeatable, owned process that reduces risk and leaves a reliable evidence trail.
WHAT THE HIPAA SECURITY RULE EXPECTS
The HIPAA Security Rule requires covered entities and business associates to conduct an accurate and thorough assessment of potential risks and vulnerabilities to the confidentiality, integrity, and availability of electronic protected health information (ePHI). It also requires implementation of security measures to reduce identified risks and vulnerabilities to a reasonable and appropriate level.
Those are separate but connected responsibilities: risk analysis and risk management. A scan can provide useful input to the analysis, but it does not establish by itself that the organization considered its ePHI environment, assessed the significance of findings, or acted on the risks.
HHS describes risk analysis as an ongoing process that should reflect changes in technology, operations, and threats. HIPAA does not prescribe one universal scan frequency or require a particular scanning product. Organizations should define a suitable process for their own environment and document how they address risk.
So, a one-time scan with no documented review or follow-through is difficult to defend as evidence of an effective, ongoing risk-management process. The missing pieces are often the decisions: what mattered, why it mattered, who accepted or treated the risk, and how the organization confirmed remediation.
See the HIPAA Security Rule, 45 CFR § 164.308 and HHS guidance on risk analysis.
WHAT CYBER INSURERS MAY ASK YOU TO PROVE
Cyber insurance requirements are not uniform. The application, policy wording, endorsements, representations, and insurer-specific security conditions determine what applies to a particular organization. Some insurers ask about vulnerability scanning, patching practices, and remediation timelines; some may seek updated information or evidence during the policy term. Do not treat one insurer’s requirement as a market-wide rule.
The operational test is straightforward: can you support the statements you make in an application or renewal? If you report that you scan systems regularly or remediate critical issues within a set period, retain evidence that shows the scope, dates, results, action taken, and any approved exceptions.
For example, Coalition’s Active Cyber policy FAQ describes a specific policy program and its vulnerability-related conditions. It is an example of why organizations should review the actual terms of their own coverage, not assume every policy has identical requirements.
Align your questionnaire answers with what your team actually does. A written policy and a scan report are not enough if the ticket history shows findings were never reviewed or if exceptions have no owner or review date.
WHAT CMMC LEVEL 2 REQUIRES
For CMMC Level 2, NIST SP 800-171 includes three directly relevant Risk Assessment practices:
- RA.L2-3.11.1: Periodically assess risk to organizational operations, assets, and individuals.
- RA.L2-3.11.2: Scan systems and applications periodically and when new vulnerabilities affecting them are identified.
- RA.L2-3.11.3: Remediate vulnerabilities in accordance with risk assessments.
That language calls for a defined, repeatable process, including scans when relevant new vulnerabilities are identified. It does not say every organization must scan continuously or fix every finding within one universal number of days. The organization defines and documents suitable frequencies and remediation priorities based on risk.
CMMC assessors look for evidence that requirements are implemented and operating, not simply for a scanner license or a PDF. Relevant evidence may include documented scan frequency, scan results, vulnerability-management records, remediation activity, and staff who can explain how findings are analyzed and addressed. The CMMC Level 2 Assessment Guide provides guidance on assessment evidence.
Be precise about plans of action as well. An operational plan that tracks deficiencies and planned corrections is not the same thing as a CMMC assessment POA&M. A POA&M does not automatically make an unmet requirement compliant; CMMC’s rules determine which requirements, if any, may be addressed through an assessment POA&M and under what conditions. Keep your vulnerability records, operational corrective-action tracking, and assessment POA&M distinct and current.
THE COMMON FAILURE: FINDINGS WITHOUT RISK DECISIONS
Many organizations can produce a scan report. Fewer can answer the questions behind it:
- Scope: Which known assets were included, and which were missed or excluded?
- Coverage: What portion of in-scope assets was scanned, and when?
- Review: Who evaluated findings and determined their business significance?
- Priority: Why did one issue move ahead of another?
- Treatment: Was the finding remediated, mitigated, transferred, or accepted?
- Ownership: Who is accountable for the next action and its due date?
- Validation: How was closure verified?
- Residual risk: Who approved an exception, and when will it be reviewed again?
Without those links, a scan report is a snapshot, not proof of a functioning management process.
WHAT DEFENSIBLE VULNERABILITY EVIDENCE LOOKS LIKE
A practical evidence set connects technical results to governance and action. Maintain records that show:
- Scope and scan coverage. Keep an asset inventory and reports showing what was scanned, what was not, the scan date, and relevant exclusions. Track coverage against known assets rather than presenting a scan percentage without a defined denominator.
- Prioritization and decisions. Record severity alongside relevant context, such as exposure, asset criticality, exploit information, and potential impact to ePHI or controlled unclassified information (CUI). Preserve the rationale for the selected priority and treatment.
- Remediation ownership and timeframes. Set organization-defined remediation targets based on risk. Track the assigned owner, due date, actual completion time, and any delay. These are your program’s targets, not a claim that HIPAA or CMMC imposes the same fixed deadline on every vulnerability.
- Validated closure. Preserve the ticket, patch or change record, and validation evidence, such as a follow-up scan, showing whether the issue was resolved. Closing a ticket is not the same as confirming the vulnerability is gone.
- Documented exceptions. For accepted or deferred risk, record the business justification, approver, interim safeguards, accountable owner, and review or expiration date. An exception should be an explicit decision, not a finding that disappeared from the spreadsheet.
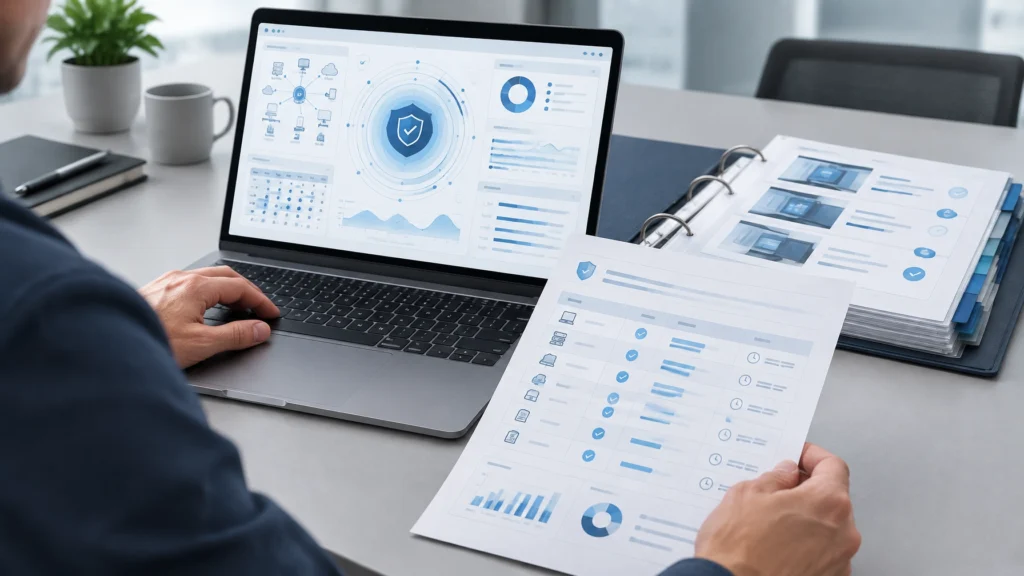
Use these records to show a connected chain: asset → finding → risk decision → owner → action → validation → residual-risk review. The exact evidence format can vary. What matters is that it is current, traceable, and consistent with your policies and the scope of your assessment.
TURN SCANNING INTO A GOVERNED PROGRAM
A defensible vulnerability-management process has people and decisions behind its tools. IT teams need clear procedures for coverage, review, prioritization, remediation, and verification. Leadership needs visibility into overdue work, unresolved exceptions, and the risks those items leave behind.
Cenova Cyber’s Vulnerability Management as a Service (VMaaS) is designed to connect discovery with risk-based prioritization, remediation tracking, validation, and compliance-oriented reporting. Our vCISO service can support the governance layer: defining accountability, aligning policies and risk decisions, and helping leadership oversee the program.
A scan report shows what a tool found. Your evidence should show what your organization decided, and what happened next.
Contact Cenova Cyber to schedule a free vulnerability management consultation. We’ll review your current process, identify evidence gaps, and help you define practical next steps for your HIPAA, insurance, or CMMC requirements. Talk with our team.
This article provides general information, not legal, insurance, or compliance advice. Requirements depend on your organization’s circumstances and applicable contract, regulation, policy, and assessment scope.