
Security Monitoring – 360° Visibility
Stop managing alerts – Start managing risk with AI-assisted log enrichment and real-time exposure mapping.
Data is Liability—Until It’s Intelligence
Most companies are drowning in log data they can’t use. Cenova Cyber’s Monitoring transforms millions of raw data points into a single, prioritized view of your organization’s security health and risk. Traditional SIEM platforms generate thousands of alerts but lack the context and response capabilities needed to stop real threats.
Without automation, enrichment, and human validation, organizations are left overwhelmed with alerts and vulnerable. Traditional SIEMs fail because they generate a high volume of alerts and require constant tuning and dedicated staff to manage. Without context and automated response capabilities, organizations are left highly exposed and vulnerable.
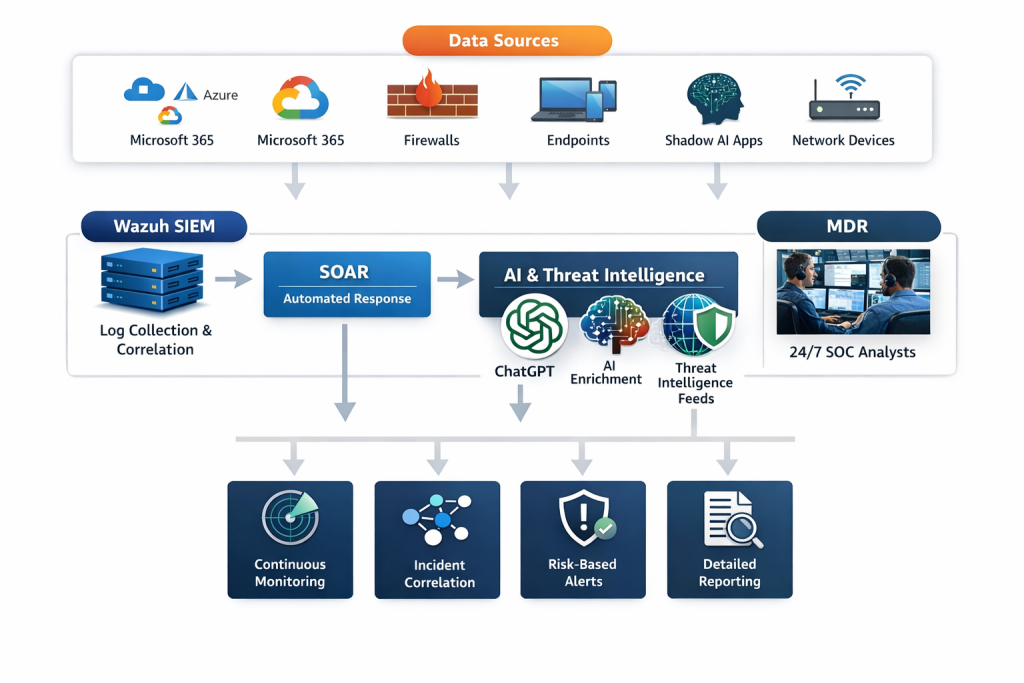
Cenova Cyber’s SOC provides 24×7 monitoring leveraging SIEM, MDR, SOAR and AI-assisted enrichment to provide event monitoring, incident response, vulnerability monitoring, threat intelligence, automated playbooks, configuration management and end point protection. A compliance-focused monitoring solution that is an MDR-backed, integrated security platform built for mid-market + defense contractors.
Cenova doesn’t just generate alerts—we investigate, validate, and contextualize them. Our SOC prioritizes incidents based on business impact and compliance exposure, ensuring your team isn’t overwhelmed by noise or blind to real risk.
What is managed security monitoring?
Managed security monitoring is a service where an outside Security Operations Center (SOC) collects and analyzes activity from your endpoints, network, cloud and Microsoft 365 around the clock, investigates anything suspicious and responds to real threats. Cenova Cyber combines SIEM, SOAR automation, AI-assisted enrichment and US-based analysts, so you get prioritized, validated incidents instead of alert noise.
How Cenova’s 24/7 monitoring works
- Collect — telemetry from cloud platforms, identity systems, endpoints and network devices.
- Enrich — AI-assisted analysis and threat intelligence add context to every alert.
- Prioritize — alerts are ranked by business impact and compliance exposure.
- Respond — US-based SOC analysts validate, contain and escalate real threats.
- Prove — monthly reporting and audit evidence for HIPAA, NIST and CMMC.
Get a free consultation
See what your logs are hiding, with no obligation.
Prefer to talk? Call (844) 236-6820 (844-CENOVA0).
How Our Platform Works
Cenova Cyber’s platform is built to support HIPAA, NIST, CMMC Level 2 and NIST 800-171 monitoring requirements, and focused on providing a compliance-driven and managed security system.
- Wazuh SIEM for centralized telemetry
- SOAR automation for correlation and response
- AI-assisted analysis for enrichment and investigation
- Threat intelligence feeds for real-time context
- 24/7 MDR analysts for validation and response
- Integrated with AWS, Azure, M365
- US Based 24/7 SOC Analysts
- Self-Hosted or Cloud Based
- Aligned with CMMC and NIST-171 requirements
- Combines SIEM, SOAR, AI-assisted analysis, and MDR
Get a SIEM Ingestion Audit
The “Visibility Gap”
Modern businesses operate across hybrid clouds, remote endpoints, and dozens of SaaS applications. This creates “Security Silos.” When a breach happens, it takes the average company over 200 days to realize it because the evidence was buried in a log file no one was watching.
Benefits of our Monitoring Solutions:
- Predictable Cost: Traditional vendors charge by data volume, punishing you for being successful and growing.
- Reduce Risk: Visibility and Focus on where the actual risk exists.
- Compliance Achieved: Provides the information needed for compliance and cyber insurance.
- Reduced Alert Fatigue: Less internal workload as your team focuses on the critical alerts.
- Lack of Context: A technical alert tells you a port is open; it doesn’t tell you that your most sensitive customer database is currently being exported.
- Threat intelligence feeds: Continuous alert enrichment and prioritization
Advanced Threat Detection & Intelligent SOC Operations
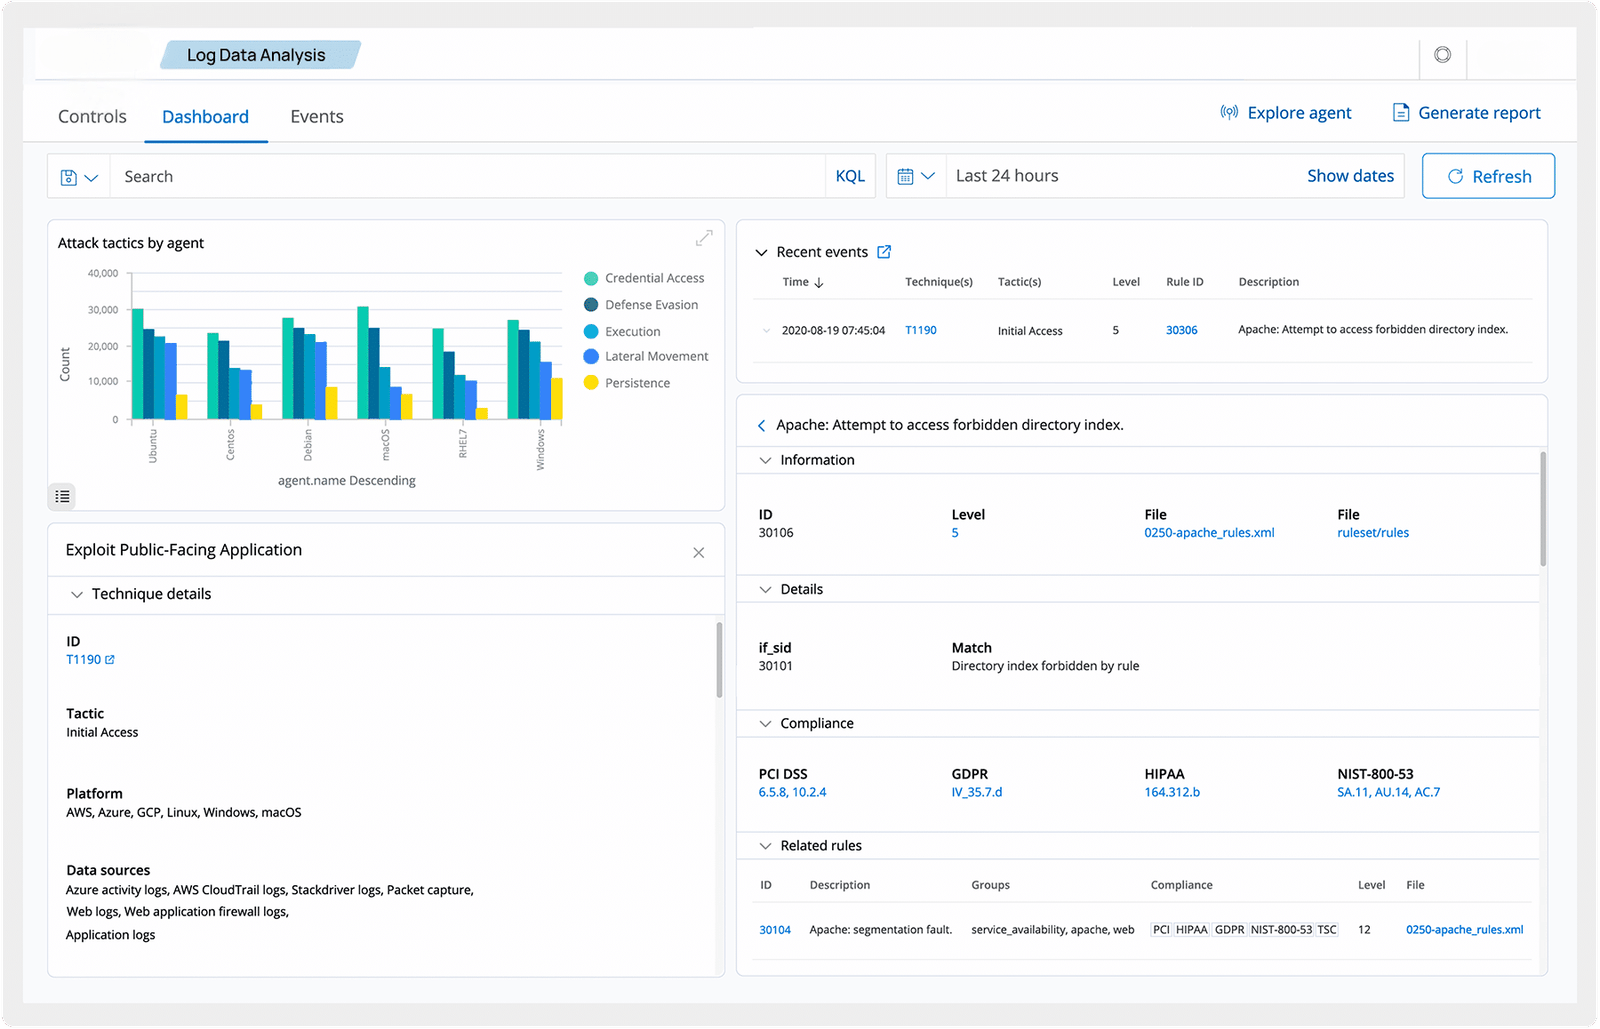
Our platform goes beyond traditional SIEM by combining Wazuh, AI-assisted analysis, SOAR automation, threat intelligence, and 24/7 MDR expertise to deliver true risk-based security operations.
1. Unified Data Aggregation
We ingest telemetry from across your environment – cloud platforms, identity systems, endpoints, and network devices – and apply AI-assisted enrichment to normalize and correlate activity across your entire stack.
2. Context-Aware Risk Prioritization
We prioritize alerts based on real business risk, incorporating threat intelligence, asset sensitivity, and behavioral indicators to ensure critical threats are addressed first.
3. Noise Reduction Through Correlation
Correlates activity across users and systems to identify suspicious patterns. We dramatically reduce alert fatigue and allow our analysts to focus on real threats.
4. Behavioral Detection
Correlates activity across users and systems to identify suspicious patterns
5. Asset-Centric Security
Threats targeting high-value systems – such as CUI environments, financial systems, and executive accounts – are automatically elevated in priority.
6. Attack Lifecycle Visibility
All activity is mapped to the MITRE ATT&CK framework, providing clear insight into adversary behavior and attack progression.
7. Continuous Threat Evaluation
As new data is ingested, alerts are continuously enriched and re-evaluated to identify evolving and low-and-slow attack patterns.
Why Your CFO Will Love Our Monitoring
- Cost-Optimized Ingestion: We use “Smart Tiering” to store high-value security data in high-performance storage while moving archival compliance data to low-cost cold storage.
- Audit-Ready Compliance: Whether it’s CMMC, NIST, SOC2, HIPAA, or GDPR, our monitoring automatically generates the configuration and vulnerability management reports your auditors need, saving your team hundreds of manual hours.
- Predictable Pricing: No “gotcha” bills for data spikes. We offer flat-rate, asset-based pricing models.
Download our Monitoring Essentials eBook here
Get a free consultation
See what your logs are hiding, with no obligation.
Prefer to talk? Call (844) 236-6820 (844-CENOVA0).
Free Guides & Checklists
Free self-assessments from the Cenova Cyber team to check how ready you are to spot and stop an attack.
Incident Response Maturity Self-Assessment
Score how ready your team is to detect, respond to and recover from a security incident.
Ransomware Readiness Self-Assessment
Check your backups, endpoint defenses, access controls and detection against a ransomware attack.
Frequently Asked Questions
(24/7 MDR, Network, SIEM, SOC, SOAR)
Q1. How is your security monitoring different from a traditional SIEM?
Traditional SIEMs generate alerts without context. Cenova combines SIEM, SOAR, MDR, and AI‑assisted enrichment to prioritize real risk and provide validated response—not alert noise.
Q2. Is your monitoring aligned with HIPAA and NIST requirements?
Yes. Our monitoring platform is built to support HIPAA, NIST 800‑171, and CMMC Level 2 security monitoring and audit evidence expectations.
Q3. Do we need our own SOC team to use your monitoring services?
No. Cenova provides a US‑based, 24/7 SOC that monitors, investigates, and responds on your behalf—or co‑manages with your internal team.
Q4. What does managed security monitoring cost?
Pricing is predictable and asset-based, so you pay for the systems we monitor, not for data volume. There are no surprise bills when your log volume spikes. A free consultation gets you an exact quote.
Q5. Which systems can you monitor?
Endpoints, servers, firewalls and network devices, identity systems, Microsoft 365 and cloud platforms such as AWS and Azure, in self-hosted or cloud-based deployments.
Q6. What happens when you find a real threat?
Our SOC analysts validate the alert, take containment steps such as isolating an affected device, and notify your team with clear next steps and a full incident report.
Get a free consultation
Talk to us about 24/7 monitoring for your environment, with no obligation.
Prefer to talk? Call (844) 236-6820 (844-CENOVA0).