
COMPLIANT CLOUD & INFRASTRUCTURE
Cloud and Infrastructure Built to Meet Compliance Requirements
Cenova Cyber designs, manages and documents your cloud and on-premise environment to support HIPAA, PCI-DSS and other frameworks, so you stay secure and audit-ready.
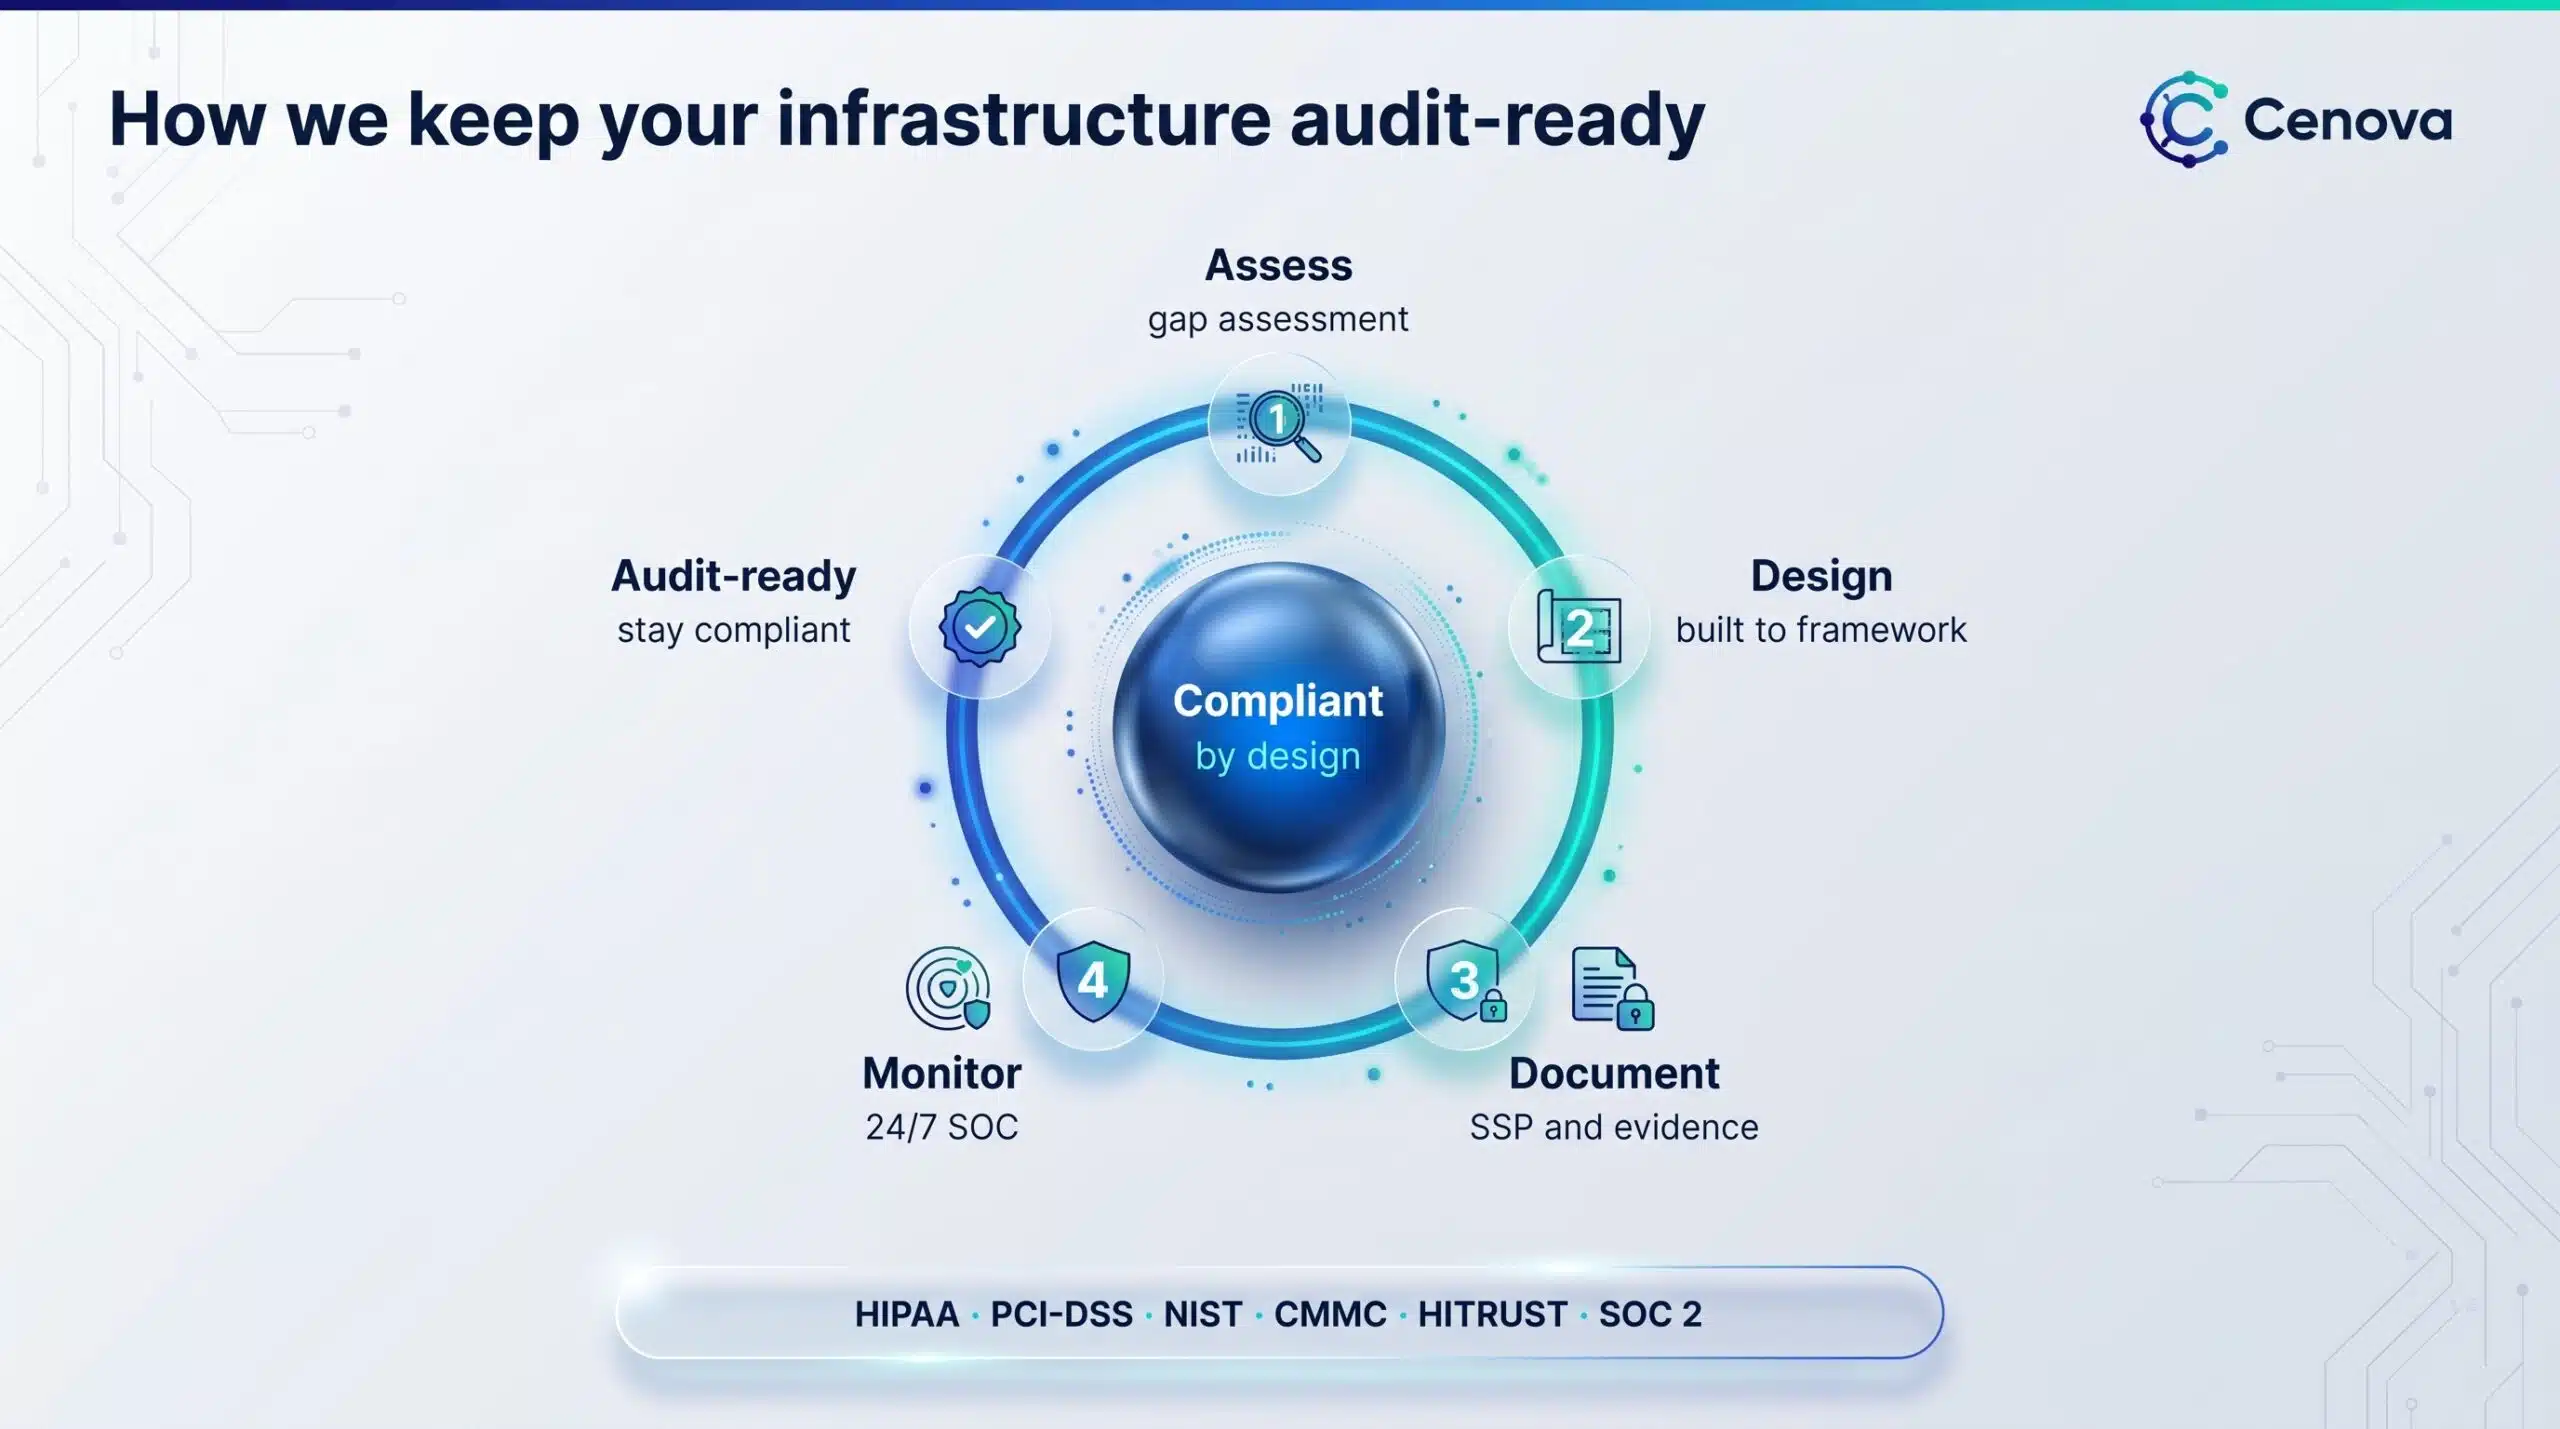
Compliant cloud infrastructure is cloud, hybrid or on-premises IT that is designed, configured and documented to meet a specific framework, such as HIPAA, PCI-DSS, NIST, CMMC, HITRUST or CJIS, so it supports how your business runs and can pass an audit.
Regulated businesses can’t bolt on compliance after the fact. It has to be built into the infrastructure itself. Cenova Cyber designs and manages cloud and on-premises environments that meet CMMC, HIPAA, HITRUST and CJIS requirements from day one, and keeps them that way.
Get a free consultation
Find out what your infrastructure needs to meet your compliance requirements, with no obligation.
Prefer to talk? Call (844) 236-6820 (844-CENOVA0).
Why Does “Compliant” Infrastructure Matter?
Most compliance failures aren’t policy problems. They’re configuration problems: missing logs, shared admin accounts, unencrypted backups, or Microsoft 365 set up with default settings. If your infrastructure wasn’t designed for your framework, it can hold your business back and still fail an audit. We build it to do both: support the way your business runs and meet the requirements you answer to.
What’s Included in Compliant Cloud & Infrastructure?
- Cloud and hybrid infrastructure design aligned to your compliance framework.
- Microsoft 365 GCC / GCC High and Azure Government configuration where CMMC or CUI requires it.
- AWS, Azure, Google Cloud and Microsoft 365 hardening against CIS and framework baselines.
- Access controls, MFA, encryption and logging built to audit standards.
- Encrypted, verified backups stored in SOC 2 Type II audited facilities.
- Documentation support for assessments and audits, including system security plans and evidence.
- Ongoing monitoring to maintain compliance posture, not just achieve it once.
- Coordination with your compliance officer or vCISO.
Moving From an On-Site Server Room to the Cloud?
Many businesses still run key systems from a server closet or small data center in their office. When it’s time to move those workloads to AWS, Microsoft Azure or Google Cloud, Cenova plans and manages the migration with security and compliance built in from the start, so nothing sensitive is exposed along the way and your new environment is audit-ready on day one.
- Readiness assessment — what to move, what to retire and what needs to stay on-site.
- Migration plan and cutover — scheduled around your business so your team keeps working.
- Secure cloud configuration — AWS, Azure or Google Cloud set up to your compliance framework.
- Documentation and ongoing management — evidence for your auditor and support after the move.
Cenova supports all three major cloud platforms: AWS, Microsoft Azure and Google Cloud.
Free Cloud Security Resources
Planning a move to the cloud or tightening the setup you already have? Start with these free guides.
Cloud Migration Security Guide
Secure your business through the move to cloud infrastructure, not just after it.
Cloud Security Configuration Checklist
Harden Microsoft 365, Google Workspace and similar platforms against the most common misconfigurations.
Which Compliance Frameworks Does Cenova Build For?
| Framework | Who it applies to | What we build in |
|---|---|---|
| CMMC Level 2 / NIST 800-171 | Defense contractors handling CUI | CUI enclaves, GCC High, access control, audit logging, SSP support |
| HIPAA | Healthcare providers and business associates | ePHI encryption, access logging, backup and recovery, BAAs |
| PCI-DSS | Businesses that store, process or transmit card data | Network segmentation, encryption, access control, logging and vulnerability scanning |
| NIST CSF | Any organization that wants a recognized security framework | Risk-based controls mapped to Identify, Protect, Detect, Respond and Recover |
| HITRUST | Healthcare and health tech organizations | Control mapping, evidence collection, continuous monitoring |
| CJIS | Agencies and vendors handling criminal justice data | Advanced authentication, encryption, audit trails |
| SOC 2 | SaaS and service providers | Security and availability controls, change management evidence |
Why Do Businesses Choose Cenova?
- Deep experience with HIPAA, PCI-DSS, NIST, CMMC Level 2, HITRUST and CJIS environments.
- Infrastructure and security expertise under one roof.
- Built for audits, not scrambling before one.
- 24/7 US-based SOC watching the environment we build.
- Hands-on support with national-level compliance knowledge.
We have been working with Cenova Cyber for the last 7 years. First as a virtual CISO and subsequently as a SIEM provider. I have always found Cenova to be professional, knowledgeable and very helpful. I would definitely recommend them.
Andrew Stead, CTO, HIPPO Technologies
Building infrastructure for a compliance deadline?
Talk to Cenova Cyber before you build it wrong.
Prefer to talk? Call (844) 236-6820 (844-CENOVA0).
Frequently Asked Questions
Q1. Which compliance frameworks do you build infrastructure for?
CMMC Level 2 and NIST 800-171, HIPAA, HITRUST, CJIS and SOC 2.
Q2. What causes most compliance failures?
Configuration problems, not policy problems: missing logs, shared admin accounts, unencrypted backups, or Microsoft 365 left on default settings. That’s why Cenova builds the framework’s requirements into the infrastructure itself.
Q3. Do we need Microsoft 365 GCC High for CMMC?
It depends on whether you store or process Controlled Unclassified Information (CUI) and what your prime contractor requires. We assess your data flows and recommend the right environment, which may be GCC High, a CUI enclave or a commercial tenant with added controls.
Q4. Can you fix our existing environment instead of rebuilding it?
Often, yes. We start with a gap assessment, then remediate what’s there where possible and rebuild only what can’t meet the standard.
Q5. Will you work with our auditor or assessor?
Yes. We prepare documentation and evidence and can join assessor meetings to explain technical controls.
Q6. Is compliant infrastructure more expensive?
Sometimes a little up front. It usually costs far less than failing an audit, losing a contract, or rebuilding under deadline.
Q7. How do we get started?
With a free risk assessment. We review your current environment against your framework and show you the gaps before anything is built or changed.
Q8. Can you migrate our servers to AWS, Azure or Google Cloud?
Yes. We plan and manage migrations from on-site servers to AWS, Microsoft Azure or Google Cloud, and configure the new environment to meet your compliance framework so it supports your business and is ready for an audit.
Related Services
CMMC Compliance · HIPAA Compliance · Virtual CISO · Vulnerability Management as a Service