
Your CMMC Score Is Not Your Compliance: Why Defense Contractors Fail the Second Assessment
A strong CMMC score can open the door to a DoD contract. It cannot keep that door open by itself.
Defense contractors often treat the initial assessment as the finish line. They build an System Security Plan, calculate an SPRS score, close a few visible gaps, and prepare for the C3PAO review.
Then the environment changes.
A new workstation is added. A firewall rule is modified. An employee downloads CUI to an unmanaged device. Vulnerability scans stop running. Logs are not reviewed. The SSP no longer reflects reality.
That is where many contractors fail the second assessment.
CMMC IS NOT A ONE-TIME PROJECT
CMMC Level 2 requires implementation of all 110 security requirements in NIST SP 800-171 Rev. 2 within the assessed environment. Depending on contract requirements, the organization must complete a self-assessment or third-party assessment through a Certified Third-Party Assessment Organization, commonly called a C3PAO.
The assessment is periodic. The responsibility is continuous.
CMMC Level 2 also requires a senior company official to submit an annual affirmation of continued compliance. That affirmation confirms that the organization continues to meet its obligations, maintain its documented security environment, and sustain the controls that supported its assessment.
In practical terms, your company must be able to answer a difficult question every day:
> Are the controls that earned our CMMC status still implemented, operating, and supported by evidence?
If the answer is uncertain, your compliance program is already at risk.
The DoD CMMC program information explains the assessment and affirmation requirements. The annual affirmation is not a routine administrative form. It is a formal statement made by company leadership.
False or misleading representations can create exposure under federal false-statement laws and the False Claims Act, particularly when inaccurate compliance claims are connected to government contract payments.
FAILURE MODE #1: TREATING THE SSP AS THE DELIVERABLE
An SSP is essential. It explains how your organization satisfies the NIST SP 800-171 requirements, identifies system boundaries, describes security procedures, and documents responsibilities.
But an SSP is not the control.
A well-written document cannot compensate for:
- Disabled multifactor authentication
- Unpatched operating systems
- Unreviewed security logs
- Incomplete access reviews
- Unmanaged endpoints
- Missing incident response exercises
- Unsupported backup and recovery processes
- Poorly controlled administrative accounts
A C3PAO will evaluate whether your documented practices match your operational environment. Evidence must demonstrate that controls are not merely planned or described. They are implemented and functioning.
Your SSP should be treated as a living management document. When the environment changes, the SSP, system boundary, asset inventory, policies, and evidence must change with it.
The document describes the defense. Your operations must prove the defense is active.
FAILURE MODE #2: USING A POA&M AS A PARKING LOT
A Plan of Action and Milestones is a remediation management tool, not a permanent storage location for unresolved weaknesses.
A disciplined POA&M identifies:
- The specific security requirement that is not satisfied
- The affected asset, system, or process
- The business and compliance risk
- The remediation owner
- The required resources
- The target completion date
- The evidence required to close the item
- The dependencies that could delay remediation
Under CMMC, POA&Ms are allowed only under strict conditions. Eligible items must be resolved within the permitted timeframe, generally 180 days, and the organization must satisfy the applicable score and control limitations.
A POA&M without ownership and deadlines is not remediation. It is deferred risk.
Contractors also make the mistake of assuming that every deficiency can be placed on a POA&M. That is not the case. Certain requirements cannot be deferred, and overdue or improperly scoped POA&M items can undermine the assessment.
Manage the POA&M weekly. Escalate blocked items. Close every item with evidence, not an email promising that the work is complete.
FAILURE MODE #3: SCOPING CUI OUTSIDE THE BOUNDARY
CMMC scope is one of the most important, and most misunderstood, parts of the process.
Many defense manufacturers begin by trying to secure the entire corporate network. Others draw a boundary that is too small and unintentionally leave CUI-connected systems outside the assessed environment.
Both approaches create risk.
Your organization must understand where Federal Contract Information and Controlled Unclassified Information:
- Enters the business
- Is received and transmitted
- Is stored
- Is processed
- Is modified
- Is backed up
- Is printed
- Is accessed remotely
- Is shared with suppliers or subcontractors
- Is deleted or archived
That requires documented data-flow mapping.
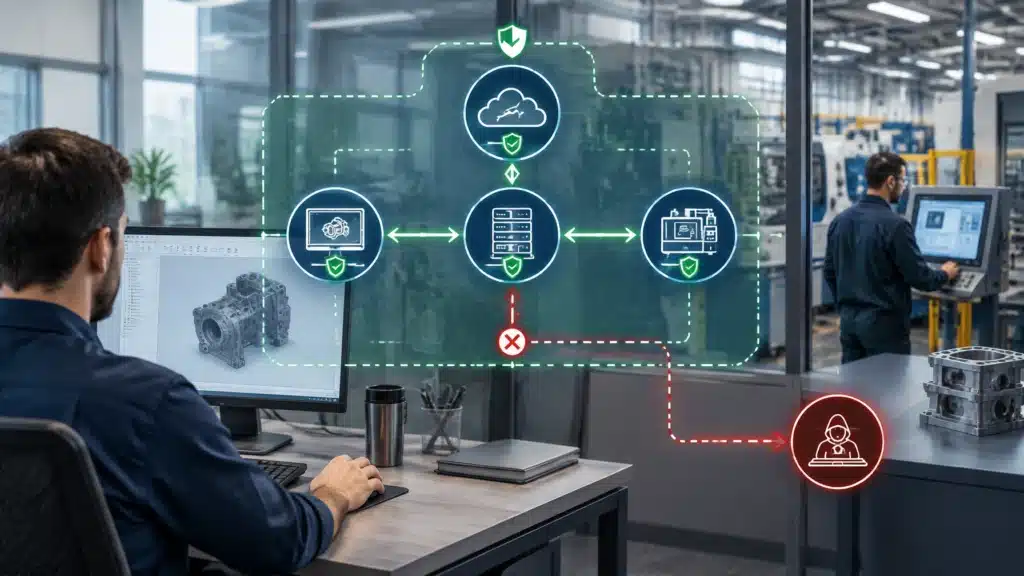
A CUI data-flow diagram should connect users, workstations, servers, cloud services, file repositories, production systems, removable media, remote access tools, and third parties. It should also show which systems are in scope, which are out of scope, and why.
Scoping errors create two opposite problems:
- Under-scoping: CUI touches a system that was excluded from the assessment boundary.
- Over-scoping: The contractor includes unnecessary systems, increasing remediation cost and operational complexity.
A defensible scope is accurate, documented, and aligned with how information actually moves through the business.
FAILURE MODE #4: IGNORING CONFIGURATION DRIFT
A compliant environment can become noncompliant after one change.
An administrator may create a temporary account and forget to remove it. A new cloud application may be connected without a security review. A firewall exception may remain open after a project ends. A production system may be placed on the same network as a workstation handling CUI.
These changes are not unusual. That is why continuous compliance requires configuration management.
A mature program maintains:
- A current hardware and software asset inventory
- Approved baseline configurations
- Change-management procedures
- System ownership assignments
- Access review records
- Security configuration checks
- Exception tracking
- Documented approval for material changes
The question is not whether your environment changes. It will.
The question is whether you detect those changes, evaluate their impact, and update your compliance evidence before an assessor discovers them.
FAILURE MODE #5: HAVING NO CONTINUOUS MONITORING
Continuous compliance depends on continuous visibility.
At a minimum, defense contractors should maintain a program that supports:
This does not mean collecting data without purpose. It means operating a repeatable process that turns security activity into defensible evidence.
Examples include:
- Monthly access review records
- Vulnerability scan results and remediation tickets
- Endpoint detection alerts and response records
- Firewall and identity logs
- Backup verification reports
- Incident response exercises
- Security awareness completion records
- Change-management approvals
- Policy acknowledgments
- Configuration compliance reports
If evidence is created only during the weeks before an assessment, it will be incomplete, inconsistent, or difficult to trust.
THE SPRS SCORE IS A STARTING POINT, NOT A SHIELD
Your SPRS score provides important context. It communicates your assessed posture against the NIST SP 800-171 requirements and helps the government evaluate supplier risk.
But a high score without evidence is a trap.
A score can look strong while:
- The assessment boundary is inaccurate
- The SSP is outdated
- CUI flows through an excluded system
- POA&M items are overdue
- Vulnerability scans are not operating
- Logs are not reviewed
- Controls are not consistently enforced
- Leadership cannot validate the annual affirmation
The score is only as reliable as the assessment process, scope, documentation, and operational evidence behind it.
Do not optimize for a number. Build a security program that can defend the number.
WHAT SUSTAINED CMMC COMPLIANCE LOOKS LIKE
A sustainable program connects governance, technology, and daily operations.
Your organization should be able to:
- Identify every in-scope asset and system.
- Map FCI and CUI data flows across the environment.
- Maintain an accurate SSP and system boundary.
- Track every deficiency through a controlled POA&M process.
- Scan continuously for vulnerabilities.
- Monitor logs and security events.
- Review access and configuration changes.
- Test incident response and recovery procedures.
- Collect evidence as controls operate.
- Give leadership an accurate basis for the annual affirmation.
This is not simply an IT responsibility. CMMC affects operations, engineering, human resources, contracts, legal, executive leadership, and third-party relationships.
The organization must own the outcome.
BUILD A CMMC PROGRAM THAT HOLDS UP BETWEEN ASSESSMENTS
Cenova Cyber helps defense contractors move from uncertainty to a defensible, sustainable compliance program.
Our phased approach includes:
PHASE 1: GAP ASSESSMENT AND SCOPING
We review your environment, identify CUI and FCI data flows, validate the assessment boundary, evaluate your current NIST SP 800-171 posture, and establish a baseline SPRS score.
PHASE 2: REMEDIATION AND ENGINEERING
We prioritize gaps, manage remediation, update documentation, strengthen technical controls, and help your team close deficiencies with evidence.
PHASE 3: CONTINUOUS COMPLIANCE
Our CMMC compliance program combines vCISO guidance with 24/7 Managed SOC capabilities to monitor the environment, identify control drift, support incident response, and maintain the evidence needed for future assessment activity.
The objective is not to create a compliance package that looks complete for one assessment.
The objective is to build a security program that remains effective when systems change, threats evolve, and your next assessment arrives.
YOUR NEXT ASSESSMENT STARTS TODAY
Do not wait until your annual affirmation is due, or until a C3PAO identifies gaps that should have been visible months earlier.
Schedule a CMMC gap assessment with Cenova Cyber. We will help you validate your scope, evaluate your controls, review your evidence, and create a practical roadmap toward sustained CMMC Level 2 compliance.
Your CMMC score is a snapshot. Your compliance program must operate every day.