Managed Detection and Response (MDR) with SOC
Stop Cyber Threats Before They Stop Your Business
24/7 Managed Detection and Response (MDR) Powered by Our Elite SOC
In today’s threat landscape, antivirus and firewall protection aren’t enough. Hackers don’t work 9-to-5, and neither should your security. Cenova Cyber provides a world-class Security Operations Center (SOC) that acts as an always-on extension of your team. We don’t just alert you to problems; we hunt, neutralize, and remediate threats in real-time.
What is managed detection and response (MDR)?
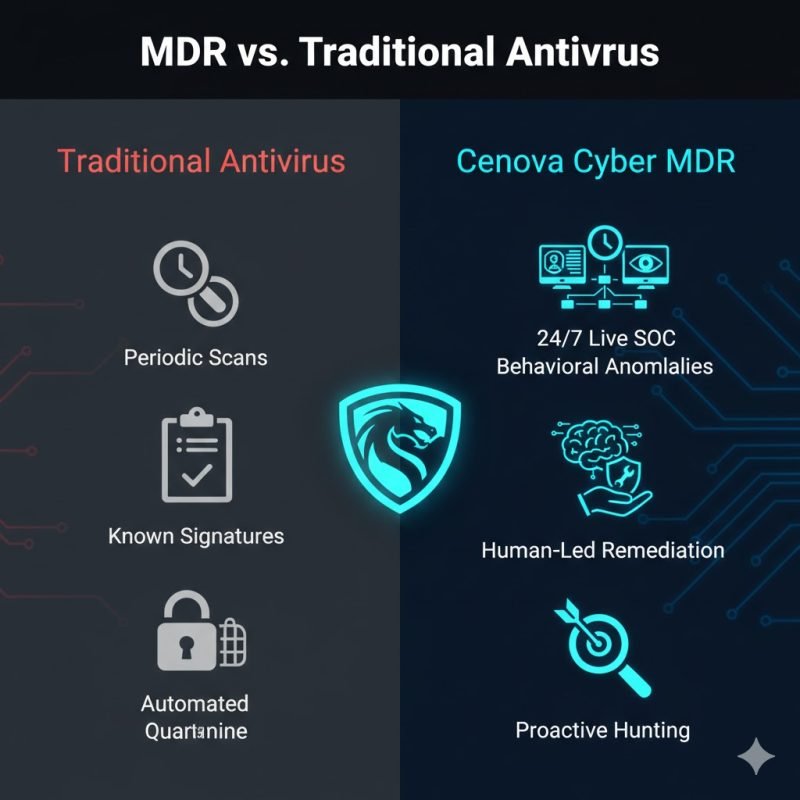
Managed detection and response (MDR) is a 24/7 service that pairs threat-detection technology with a team of security analysts who watch your environment, hunt for attackers and take action to contain threats. Unlike antivirus, which blocks known malware, MDR finds and stops attacks that slip past your defenses, reducing the time an attacker can stay hidden from months to minutes.
How MDR with Cenova’s SOC works
- Detect — endpoints, network and cloud activity are monitored 24/7/365.
- Investigate — analysts validate alerts and hunt for hidden attackers.
- Contain — confirmed threats are stopped by isolating devices and blocking malicious IPs.
- Remediate — we guide clean-up and close the gap that let the attacker in.
- Report — detailed incident and forensics reports for leadership and auditors.
Get a free consultation
Get a professional assessment of your security posture, with no obligation.
Prefer to talk? Call (844) 236-6820 (844-CENOVA0).
Why Your Business Needs MDR + SOC
Traditional security is reactive—it tells you after you’ve been hit. Our MDR service is proactive.
- The Skills Gap: Finding and keeping tier-1 security analysts is expensive and difficult. We provide the expertise for a fraction of the cost.
- Alert Fatigue: Most IT teams are buried in “noise.” We filter out the false positives and only act on what matters.
- Dwell Time: The longer a hacker is in your system, the more damage they do. We reduce “dwell time” from months to minutes.
Our SOC Core Capabilities: The Cenova Cyber Advantage
1. 24/7/365 Continuous Monitoring Our analysts monitor your endpoints, network, and cloud environments around the clock. If an anomaly occurs at 3:00 AM on Christmas, we’re already on it.
2. Proactive Threat Hunting We don’t wait for an alarm. Our experts use global threat intelligence to actively “hunt” for hidden attackers who have bypassed traditional defenses.
3. Rapid Incident Response & Containment When a threat is confirmed, we don’t just send an email. We take immediate action—isolating infected devices and blocking malicious IPs—to stop the spread before it becomes a breach.
4. Advanced Behavioral Analytics (AI + Human Intelligence) We combine cutting-edge AI that identifies “weird” behavior with human intuition to catch zero-day exploits and fileless malware that automated tools miss.
Download our MDR Essentials eBook here
Get a free consultation
Get a professional assessment of your security posture, with no obligation.
Prefer to talk? Call (844) 236-6820 (844-CENOVA0).
The “Cenova Cyber” Promise
- No Contracts, Total Flexibility: We believe in earning your trust every month. If you aren’t satisfied, you aren’t locked in.
- Day-One Protection: Our onboarding is streamlined to get your SOC coverage live immediately.
- Compliance-Ready Reporting: Detailed forensics and incident reports that satisfy auditors for HIPAA, SOC2, CMMC, and PCI.
Free Guides & Checklists
Free resources from the Cenova Cyber team to help you respond fast when an attack gets through.
Ransomware Response Playbook
What to do in the first hours after a ransomware detection, and how to recover with less damage.
Incident Response Plan Template
A fill-in template to build or update your organization’s incident response plan.
Frequently Asked Questions
Q1. How is this different from Managed IT?
Managed IT focuses on uptime and performance (making sure things work). MDR focuses on security (making sure things are safe). You need both to be truly protected.
Q2. Do I need to replace my current IT team?
Absolutely not. We act as a “force multiplier” for your internal IT or current provider, giving them the specialized security data they need to keep your company safe.
Q3. What is the difference between MDR and antivirus?
Antivirus blocks known malware on a single device. MDR combines advanced detection with human analysts who investigate suspicious behavior across your whole environment and respond to attacks antivirus misses, such as fileless malware and stolen credentials.
Q4. Is MDR monitored around the clock?
Yes. Cenova’s SOC monitors your endpoints, network and cloud environments 24/7/365, including nights, weekends and holidays.
Q5. Will MDR help with compliance and cyber insurance?
Yes. Our incident and forensics reporting supports HIPAA, SOC 2, CMMC and PCI requirements, and gives cyber insurance carriers the evidence of 24/7 monitoring and response they increasingly ask for.
Talk to a Cenova Cyber expert
Tell us about your environment and a Cenova Cyber engineer will get back to you quickly.
Prefer to talk? Call (844) 236-6820 (844-CENOVA0).